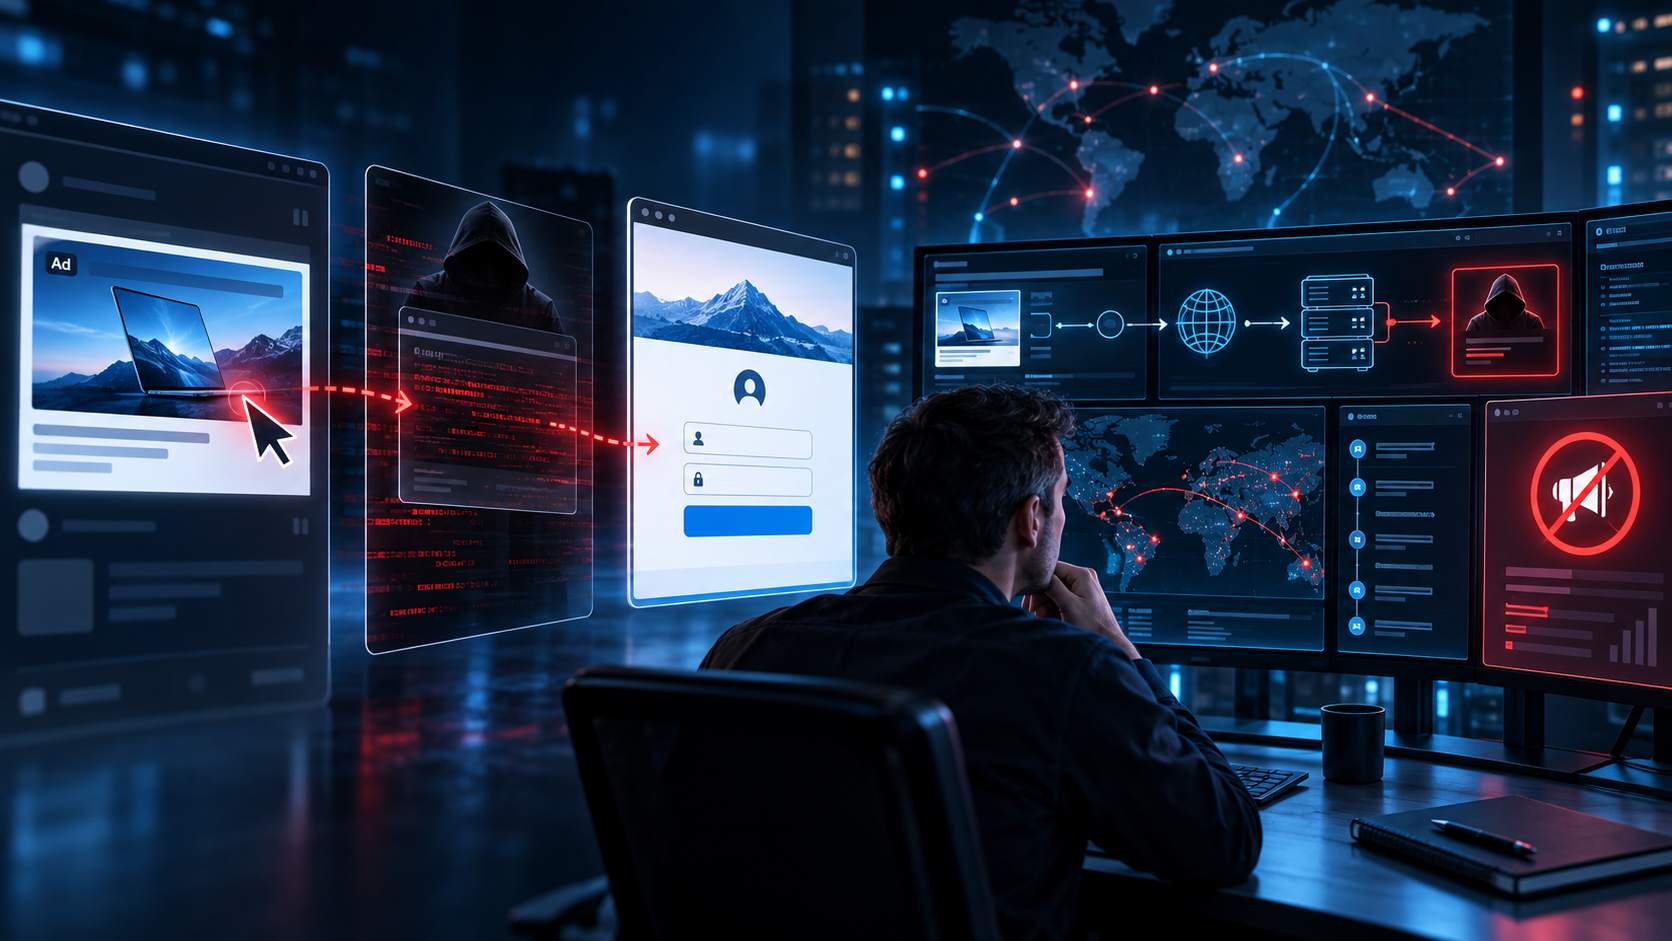
The ad sits above your own organic result. It carries your name, your colors, and a display URL that reads correctly to anyone scanning a results page, and the person who clicks it believes they're on their way to your login screen. Nobody in your organization bought it.
That's malvertising, which is paid advertising used to deliver something harmful, and here the harmful thing is an impersonation of you. It falls between two teams. Marketing owns the ad accounts and watches performance, and security owns the domains, the hosts, and the abuse reports. A fake ad in your name belongs to neither queue.
Knowing how to prevent malvertising starts with knowing who can remove what. The ad network can pull the placement and suspend the account behind it. A registrar can act on the domain, and a hosting provider can take the content offline.
Those three levers sit with three organizations that don't coordinate with each other, and each one wants different evidence. A report that reaches only the first clears the placement and leaves the operation intact, because the destination is still there waiting for the next ad account.
A fake ad campaign has three parts, all built in advance
The placement is the last thing an operator buys, not the first. Everything it points at is built and tested before a single impression serves, which is the reason a report that stops at the ad buys so little time.
It starts with a domain registered ahead of time, usually one letter or one word away from yours. Interisle's Phishing Landscape 2025 study found that 77% of phishing domains were registered specifically to commit the crime rather than being legitimate sites someone had compromised. The FBI has warned since 2022 that criminals buy search ads using a domain similar to a real business, which then sits at the top of the results page with minimal distinction from an organic listing.
The destination comes next, and it decides at request time who sees what. Google's own rules call this cloaking and define it as showing different content to different people, or to Google, to hide something that breaks the rules. A reviewer following your complaint from a corporate network gets the harmless page. Your customer, arriving from the ad on a phone, gets the credential form.
Last comes an ad account, either newly created or taken over from a legitimate advertiser. Bidding on your brand name isn't by itself the violation, since Google's trademark policy lists using trademarks as keywords among the things it won't restrict, and it won't restrict a trademark sitting in the second-level domain of the display URL either. The policy also requires the trademark to appear in the ad itself, not only on the landing page, so a trademark complaint has to rest on the ad text. Where the impersonation lives on the destination instead, that's a misrepresentation report, which is a different form and a different standard. Bolster AI published a worked example of Google Ads campaigns impersonating Amazon and Adidas, down to the misspelled domain the ads pointed at.
Do the unglamorous inventory before you file anything
You can't argue an ad is fraudulent unless you can describe the genuine version precisely, so somebody has to keep a current picture of what your legitimate advertising looks like. Most of that is inventory, and it decays quietly between campaign cycles unless one person owns keeping it current.
- Registered trademarks and the jurisdictions each one covers, because complaint forms ask for the registration.
- Every domain, subdomain, and app listing you own, plus the one canonical destination customers should reach for logins, downloads, and payments.
- Authorized ad accounts, agencies, and affiliates, so an aggressive partner doesn't get reported as an impersonator.
- A named owner for detection triage and a named owner for enforcement, including who approves escalation outside business hours.
- A customer-facing page for reporting suspicious ads, routed into the queue your analysts already work.
Two of those get skipped most often. A baseline of your own paid search footprint in the regions where you advertise is what makes an unfamiliar placement obvious, and an agreed after-hours approval path keeps a Friday night campaign from running until Monday. Notification when a domain one character away from yours is registered is the earliest signal available, and the FBI's 2022 alert tells businesses to use domain protection services that flag those registrations.
Standing to complain matters too. Google routes rights holders and their authorized representatives through a trademark troubleshooter to the right form, and Microsoft Advertising's intellectual property complaint form requires the filer to declare they're legally authorized to act for the owner. Work out who that is before the night you need them.
Detect the version your customers see
Watching for a fraudulent ad is a different job from watching for a lookalike domain, because the malicious page is served conditionally rather than continuously. A crawler arriving from a data center address, with no ad click behind it and none of the fingerprints a real browser leaves, is the visitor the filter was built to catch. It gets the clean page, and the report comes back empty.
A contributor analysis in APWG's Q1 2026 report describes the same behavior across phishing sites generally. Alongside geo and IP blocking, an increasing number of sites only show fraudulent content when the referrer is a certain site or kind of site, with search engines and social platforms given as the examples. The referrer is just the place a visitor arrived from, and an ad click is one, so a check without it tests a page the campaign never meant to show anybody.
The filter keys on a short list of signals, and they are the same signals a check has to match: a residential or mobile network path rather than a data center one, the countries where your customers live, a realistic device profile, and the click path from the placement itself. Ad targeting is granular enough that a campaign aimed at one market stays invisible to monitoring that only looks from another.
Bolster AI's fraudulent ads monitoring surfaces ad fraud impersonating a brand across paid search, sponsored placements, and social channels, and analyzes redirect chains, linked malware, and host infrastructure behind the click. Whichever tooling you use, Bolster AI included, ask which networks, countries, and devices the check runs from.
Customer reports stay the highest-signal input available, because customers meet the malicious page under exactly the conditions automation struggles to reproduce. People do report impersonation when they have somewhere to send it: nearly one in three fraud reports the FTC received in 2025 were about imposter scams, with reported losses reaching $3.5 billion.
What the ad network can and can't do
Reporting the ad is the easiest lever to pull and the narrowest. Anyone can report an ad from the placement itself, from My Ad Center, or from the Ads Transparency Center, and Google confirms receipt by email before reviewing it. Those reports get more attention than they used to: Google's teams took action on four times as many user reports in 2025 as in the year prior.
A trademark complaint reaches further than a single placement. If Google reviews one and decides to restrict the trademark, the restrictions generally apply on an ongoing basis to ads using the same second-level domain in their final URL. That's the domain the click lands on, so the restriction catches the operator's other creative aimed at the same destination. A misrepresentation finding goes further still: impersonating other brands in ads or on the destination site gets accounts suspended on detection without prior warning, and cloaking is treated the same way.
Scale shapes how any of this gets handled. Google reports blocking or removing more than 8.3 billion ads in 2025, including more than 421.5 million actioned under its Misrepresentation policy and another 372.7 million under Trademark, and says its systems caught over 99% of policy-violating ads before they ever served. The campaign in front of your customers got through all of that, which is why specific evidence outperforms strong language.
Other networks have their own doors, and picking the wrong one costs a cycle. Microsoft Advertising routes trademark complaints and reports of spam or malicious ads to two different forms, so find the right one before you write the report.
Social feeds run the same play, and the ad is often the hook. FTC data shows that shopping scams were the most reported type of social media scam in 2025, and more than 40% of the people who lost money to one reported ordering something they saw in a social media ad.
None of those actions touches the domain or the host. The destination stays live for the next ad account, for the text message and email versions of the same campaign, and for organic traffic. That gap is where a closed ad report becomes a fraud that's still running.
The registrar and the host are the other two levers
The domain sits with a registrar, and for generic top-level domains such as .com and .net, a contractual duty is attached to it. Since April 5, 2024, amendments to ICANN's Registrar Accreditation Agreement and base Registry Agreement have required registrars to confirm receipt of an abuse report and, when they hold actionable evidence that a domain is being used for phishing, to promptly take mitigation action. Country-code registries like .uk and .de set their own policies, so an identical report can land very differently.
Hosting providers control the content and carry no equivalent obligation, which makes the evidence package the whole argument. An abuse desk needs the exact URL, a capture taken under victim conditions, the redirect chain, and the trail tying that page to infrastructure the provider controls. Removing the redirector, the hop that sits between the click and the landing page, often disables several campaigns at once, a better return than chasing ad accounts an operator replaces the same afternoon.
A fourth lever reduces harm without removing anything. Reporting the URL to Google Safe Browsing puts it in front of the service that shows browser warning screens on dangerous sites, which Google says helps protect over 5 billion devices every day. A warning in front of the page suppresses real traffic while nobody has answered your report, so treat it as first aid.
When the report comes back unsubstantiated
The most common rejection has a single cause. A reviewer opened your link from a corporate network, saw the version the filter serves to reviewers, and closed the case. Nothing in that outcome says the campaign isn't real.
Recovering from it means presenting a comparison instead of an assertion: the benign response beside the malicious one, with matching timestamps, source geography, device profile, and the referrer from the ad click. Name the technique explicitly, because a reviewer reading the word cloaking with evidence attached moves faster than one reading a description of it. Pull the other two levers in parallel rather than waiting for the network to change its mind.
Then assume recurrence. Operators keep the creative, the kit, and the target list, so the question after a removal is whether the same fingerprints have reappeared under a new registration. Bolster AI's automated takedown flow sends the fraudulent URL with proof-of-fraud attributes to global blocklists and keeps watching so that removed sites, accounts, and apps don't get revived.
Where the landing page is a login clone, treat it as credential phishing against your customers rather than an advertising problem. The ad is only the acquisition channel.
The questions that tell you it's working
Report counts rise whenever attacker volume rises and say nothing about whether customers were protected. Put the list below to your own team, and to any vendor you're considering, Bolster AI included, when you're working out how to prevent malvertising rather than just log it.
- How long from an ad going live to confirmed detection, and did the detection see the malicious page or the clean one?
- How long from detection to verified removal, measured separately for the ad network, the registrar, and the host?
- Of those detections, how many were confirmed under victim conditions, and from how many vantage points?
- What happens when a network closes the report as unsubstantiated, and what does the second submission add?
- Who has to authorize a trademark complaint on your behalf, and how narrowly can that authorization be scoped?
- How often does the same operator come back under a new domain, and how quickly is that caught?
Read the answers together rather than one at a time. A fast removal time next to a high rate of customer-reported incidents usually means detection is narrower than enforcement, and a falling recurrence rate is the clearest sign that requests are reaching infrastructure instead of symptoms. The placement is the cheapest part of the operation to replace, which is why the domain, the destination, and the accounts behind it are where prevention happens.
Bolster AI detects external threats including phishing sites, lookalike domains, fraudulent social accounts, fake mobile apps, fraudulent ads, and marketplace abuse, connects related infrastructure into a single campaign, and removes them. Detection and takedown run as one workflow rather than as two separate promises, with automation carrying the volume and Bolster AI analysts handling the cases that need judgment.
If you'd rather watch a fraudulent ad get traced from placement to host on a live platform than read the sequence, book a demo and bring the campaign your team reported and couldn't get removed.
TL;DR: How to prevent malvertising starts with accepting that no single party can end the campaign. The ad network can pull the placement, the registrar can act on the lookalike domain, and the hosting provider can take the landing page offline: three separate requests with three different evidence requirements. Detection has to arrive looking like a customer, because these destinations show a reviewer a clean page and a real visitor the credential form. The standing work is what makes enforcement possible: a current picture of your legitimate advertising, a named person authorized to file trademark complaints, a customer reporting channel your analysts work, and monitoring that catches the domain before the ad serves.