The most costly executive impersonation cases rarely begin with anything technically impressive, which is part of why they are so hard to argue about internally. Adaptive Security's analysis of executive impersonation attacks records that in 2024, Arup lost $25 million after attackers used a deepfake of the chief financial officer to convince a finance employee to approve transfers during a video conference. The groundwork for an attack shaped like that is assembled almost entirely in public, out of headshots, job titles, biographies, conference appearances, and posting habits that anyone can copy in an afternoon. A fake profile is the cheapest component of the whole operation, and it is also the one component a security team can actually remove.
Removing it reliably, at the volume most large organizations now face, is an operational discipline rather than a single button press. It depends on knowing exactly who you are protecting, watching the right surfaces continuously, classifying what you find with enough precision to justify enforcement, and pushing requests through platform channels in a form that trust and safety reviewers can act on quickly. Those steps have to happen in that order, with provisions for the awkward cases where a platform says no or the person being impersonated no longer works for you.
What You Need Before Starting a Takedown Workflow
Most stalled impersonation programs are not short of detections; they are short of the authority and reference material needed to act on them, so the preparation phase matters more than it sounds. Adaptive Security frames the opening month of a CISO hardening plan around exactly this kind of groundwork, recommending a risk assessment that inventories the digital footprint of key leaders and establishes baseline verification policies before anything else gets deployed. Treat that as your entry condition, because a takedown request without documented authorization and a canonical reference point is a request a platform can reasonably ignore. Before the first alert reaches your queue, you want the following in place:
- A named owner for executive impersonation, with a documented escalation path into legal, communications, and physical security.
- Written authorization from each protected executive allowing your team to act as their agent in platform reporting.
- Verified business or brand accounts on every platform where you intend to file requests, since unverified reporters wait longer.
- An evidence standard covering screenshots, full profile URLs, account identifiers, timestamps, and any contact attempts with employees or customers.
- Severity thresholds that distinguish a dormant fake profile from an account actively soliciting money, credentials, or meetings.
Phase 1: Build the Executive Identity Baseline
Detection is a comparison exercise, and it fails without something authoritative to compare against, so the first real work is documenting what each protected leader legitimately looks like online. For every executive in scope, record the exact profile URLs and account identifiers they genuinely control on each platform, the current and prior profile photographs, the vanity handles they have used historically, and the verification status of each account. Add the variants an attacker will plausibly reach for, including nicknames, initials, married and maiden names, transliterations into other alphabets, and the punctuation tricks that let a handle read correctly at a glance while resolving to something entirely different. Capture the public footprint alongside the accounts themselves, because conference bios, earnings call photography, and recorded interviews are the raw material used to make a convincing clone.
The baseline should also note which executives carry elevated exposure for reasons that have nothing to do with technology. A chief financial officer whose signature authority is publicly documented, a chief executive who posts frequently, and a head of talent whose role makes unsolicited recruiting messages look normal all attract different impersonation pretexts. Recording that context in the baseline gives your analysts a reason to prioritize one alert over another later, and it gives you a defensible answer when leadership asks why a particular profile was escalated within an hour while another sat in the queue overnight. Keep the baseline in a system your monitoring configuration reads from, not in a spreadsheet that ages quietly after the first quarter.
Phase 2: Configure Continuous Social Monitoring
With the baseline in place, monitoring becomes a matter of coverage and tuning rather than guesswork. Configure detection against names, handle variants, and profile imagery together, because attackers routinely pair a correct headshot with a mangled handle or a correct handle with a generated portrait, and matching on only one signal leaves half the campaign invisible. Extend coverage past the obvious professional networks into short-form video, messaging platforms, regional networks, and the newer accounts that spin up faster than any manual review cycle can follow. Fuzzy matching earns its keep here, but so does suppression logic, because an alert queue that fills with fan pages, parody accounts, and legitimate employee profiles will train your analysts to skim instead of investigate.
Expect volume rather than isolated incidents, and design the queue accordingly. One financial services team, quoted in published research on executive impersonation protection and monitoring, described their situation directly: We have a massive volume of fake profiles [of our executives], and it is very important for the reputation of our company. That framing is the right one operationally, since a monitoring configuration built for occasional single-profile discoveries will collapse the first time a coordinated campaign registers forty accounts in a weekend. Route alerts by executive, platform, and severity, and make deduplication automatic so that one campaign presents as one investigation.
Phase 3: Investigate and Classify Each Alert
Investigation exists to answer three questions before enforcement begins: whether the account is genuinely impersonating a protected individual, what the account is being used to accomplish, and how far the activity has already reached. Start with the comparison against your baseline, checking the account identifier, creation date, posting history, follower composition, and whether the imagery is lifted, altered, or synthesized. Then look outward from the profile itself, because impersonation accounts are usually one component of a broader attack campaign that also includes lookalike domains, phishing pages, or messaging accounts used to move the conversation off platform. Documenting those connections during investigation is what allows a single enforcement action to break several parts of the infrastructure at once.
Classification should follow intent, since intent determines both urgency and the enforcement channel you use. A profile posting investment advice under your chief executive's name is a fraud problem aimed at customers and retail investors, while a profile messaging your finance team to arrange an urgent call is the opening move of a business email compromise attempt that may eventually involve synthetic audio or video. The Arup case is the reference point for that second category, because a deepfake of the chief financial officer was persuasive enough to carry a finance employee through approvals on a live video conference. Record whether contact has been attempted, who was contacted, and what was asked for, then set severity on the basis of that reach rather than on the sophistication of the fake.
Phase 4: Submit Platform Takedown Requests
Platform enforcement is a documentation exercise, and requests fail for procedural reasons far more often than for substantive ones. Every major platform maintains a distinct reporting path for impersonation of a person, which is not the same path as trademark infringement, spam, or fraudulent advertising, and filing under the wrong policy is the fastest way to receive a rejection that looks like a judgment on the merits. Submit under the policy clause that actually matches your classification, and make the reviewer's decision as mechanical as possible by supplying the evidence they need in one pass:
- The full URL and account identifier of the impersonating profile, captured with a timestamp.
- The URL of the executive's authentic profile, so the reviewer has a direct comparison.
- Proof of the executive's identity and of your authorization to report on their behalf.
- Screenshots of the impersonating content, including any messages sent to employees, customers, or partners.
- A short statement of harm that names the specific policy being violated.
Log every submission with its ticket reference, submission time, and platform response, because that record is what turns escalation into a factual conversation rather than a complaint. Where a platform offers a brand or rights holder program, an API, or a partner submission channel, use it for bulk campaigns instead of filing dozens of individual consumer reports that land in the same general queue. Resist the temptation to resubmit the same request repeatedly while it is pending, since duplicate filings frequently reset position in the queue and can flag your reporting account as abusive.
When a Platform Refuses or Ignores a Takedown Request
Refusals and silence are a normal part of this workflow rather than a sign that something has gone wrong, and the response to both is the same: strengthen the evidence, then widen the pressure. Reread the rejection against the policy you cited, because most denials come down to insufficient identity proof, an ambiguous comparison to the real account, or a claim filed under a clause the content does not clearly violate. Resubmit with the specific gap closed, quoting the policy language and attaching any new evidence of active harm, such as messages the account has sent to your employees since the original filing. If the platform remains unresponsive, escalate through named trust and safety contacts, your advertising or partner relationships, or counsel correspondence that documents the pattern of unactioned reports.
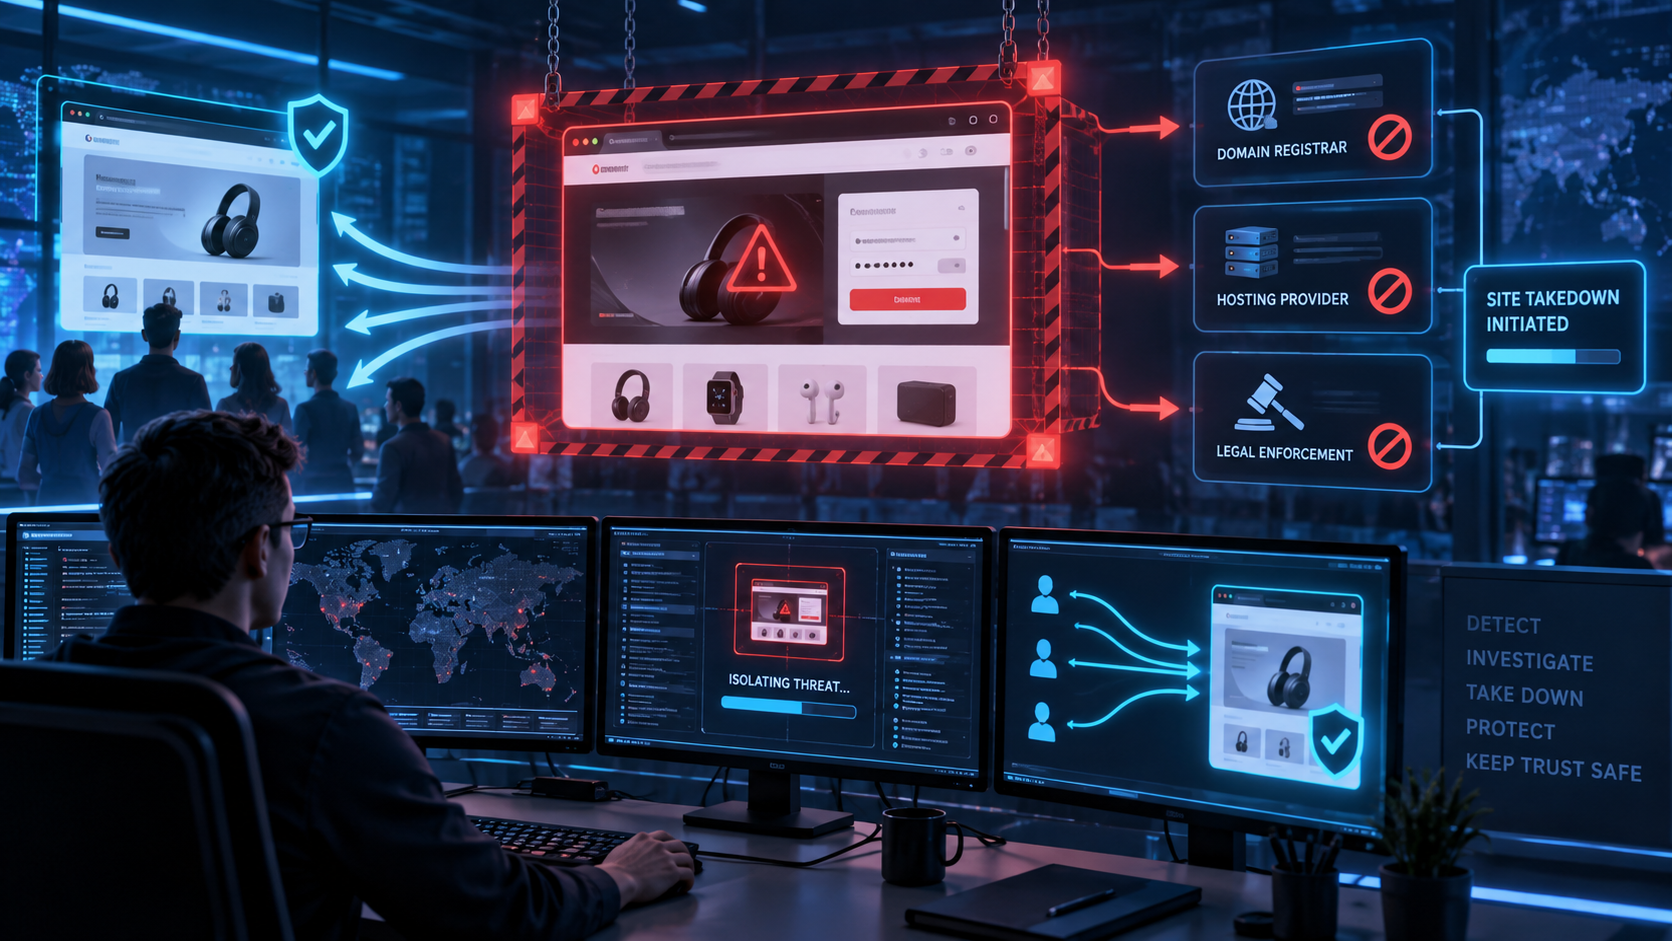
Enforcement should not stall while you wait, because the impersonation account is usually only the visible surface of the campaign. Pursue the supporting infrastructure in parallel through registrar and hosting complaints against any lookalike domains, and notify the payment providers or app stores involved if the scam routes through them. Where money has moved or been solicited, law enforcement reporting is worth the effort on its own terms and also strengthens later platform escalations; the FBI classifies business email compromise among the costliest cybercrime categories in the United States, with losses exceeding $2.9 billion in 2024 alone, and its Internet Crime Complaint Center logged 859,532 complaints in 2025 with total losses above $16 billion. In the meantime, warn the people being targeted, since a direct advisory to finance, executive assistants, and affected customers removes the attacker's advantage even while the profile stays live.
Handling Impersonation of Former Executives and Board Members
The hardest requests to file are the ones where your legal standing is thinner than your operational interest, and impersonation of departed executives and non-employee directors falls squarely into that gap. Platforms treat impersonation of a person as a matter for that person or their authorized representative, so a company reporting a fake profile of a chief financial officer who left eighteen months ago often cannot demonstrate the authority the reviewer requires. Solve this before you need it by folding identity authorization into offboarding, asking departing executives to maintain a reporting authorization for a defined period, and securing the same authorization from board members when they are appointed rather than after an incident starts.
Keep former leaders in monitoring scope for as long as their association with the organization remains commercially useful to an attacker, which is usually far longer than the exit interview suggests. Testing matters here too, since a pretext built on a familiar former name bypasses the instinct that a stranger would trigger. Adaptive Security's plan puts this in the refinement stage, recommending phishing simulations aimed at key departments such as finance, human resources, and legal using deepfakes of executives, and those exercises are considerably more revealing when one scenario impersonates someone the team remembers fondly and no longer expects to hear from.
The Done State and Ongoing Verification
A takedown is not finished when a platform confirms removal, because confirmation and disappearance are separate events and attackers rebuild faster than most closure processes assume. Verify removal yourself from an unauthenticated session and from outside your corporate network, then check again after several days, since suspended accounts are sometimes restored on appeal and cached content can remain reachable through search and syndication. Archive the full evidence package against the case rather than the individual profile, so that the next investigation into the same actor starts with the imagery, handle patterns, and infrastructure you already documented. Close the loop internally as well, telling the executive, their assistant, and any employee who received contact that the account is gone and what to do if it returns.
Then measure the program on the numbers that reflect exposure rather than effort. Time from profile creation to detection, time from detection to submission, time from submission to removal, and recurrence rate per executive will tell you whether your monitoring configuration and your enforcement channels are actually working, and they give you something concrete to report when leadership asks what the investment bought. That reporting has become part of the job description; published research on social media impersonation found that 29% of CISOs report they could lose their job if brand damage occurs from online threats, even where the incident was outside their direct control, and the same body of work notes that fake brand pages remain the most common entry point into these campaigns. Set against an average data breach cost above $4 million and impersonation-driven fraud consuming 9.8% of revenue at United States companies, a 46% increase year on year, the case for continuous coverage argues itself.
The realistic done state, then, is a steady operating rhythm rather than an empty queue: baselines refreshed as leadership and platform presence change, monitoring tuned as new networks gain traction, enforcement channels exercised often enough that escalation contacts know your name, and simulations that test whether your finance, human resources, and legal teams verify before they act. If you want to see what detection through takedown looks like as one workflow across domains, social platforms, apps, and marketplaces, request a demo from Bolster.
TL;DR: Shutting down executive impersonation across social platforms requires a repeatable operational discipline built on continuous monitoring, precise classification of fake profiles, and coordinated takedown requests submitted through official platform enforcement channels before attackers can weaponize stolen identity assets.