A customer forwards a link. The site has your logo, your product photos, maybe your homepage copied line for line, and it's selling something, offering support, or quietly collecting logins. That's website impersonation: a site presenting itself as your brand, or an authorized part of it, without your permission. The first instinct is to email the operator, who is the one party with no reason to answer.
Removal happens because a third party decides to act, and which third party depends on what the site is doing rather than on how closely it resembles you. This guide is organized around that fork: the route for a credential-harvesting page is a contractual one that doesn't exist for a counterfeit storefront, and a trademark complaint that can win a domain does nothing against a copied page on somebody else's platform.
Decide what the site is doing before you decide who to tell
Sort the site into a category first, because the category sets your grounds and your venue. A cloned website reproduces your pages and assets, while a counterfeit storefront sells goods under your name and takes payment. Fake support or partner sites route customers to someone else's phone number or ticket form. Then there are lookalike domains parked with your logo, and phishing pages collecting passwords, card numbers, or one-time codes.
Rule out the false positives before anything leaves your queue. Franchise microsites, an agency's staging server, and an authorized reseller with sloppy branding all get reported as impersonation, and a report withdrawn for inaccuracy costs you standing with the abuse desk you'll need next month.
The phishing case has a route of its own. Since April 5, 2024, amendments to ICANN's Registrar Accreditation Agreement have required accredited registrars for generic top-level domains (gTLDs) to confirm receipt of abuse reports and to promptly take mitigation action when they hold actionable evidence of DNS abuse, which the amended agreements define, and ICANN's compliance advisory explains, as malware, botnets, phishing, pharming, and spam used to deliver any of those. If the site is harvesting logins, card numbers, or one-time codes under your name, the phishing site takedown route applies, and the registrar is your fastest lever.
Nothing in that definition covers a clone that sells counterfeit goods, a fake support line, or a logo on a parked page. Those sites aren't DNS abuse, so the registrar has no contractual duty to suspend them, and many will say so. A storefront that takes card details and never ships sits in a gray zone; describe the card harvest in the report and let the registrar decide whether it's phishing. What remains is the hosting provider on terms-of-service and intellectual property grounds, the platform if the site sits on a website builder or a free tier, a DMCA notice for copied content, and, for the domain name itself, a trademark dispute or a court action.
One more check can change the venue. Interisle's 2025 phishing study found that 77% of phishing domains were registered specifically for the attack, against 23% that were legitimate domains someone had compromised. A compromised domain usually belongs to a legitimate business, so suspending it at the registrar takes an innocent site offline with the fake page. That request goes to the host and the site's owner, scoped to the offending path.
Build one evidence package and adapt it per venue
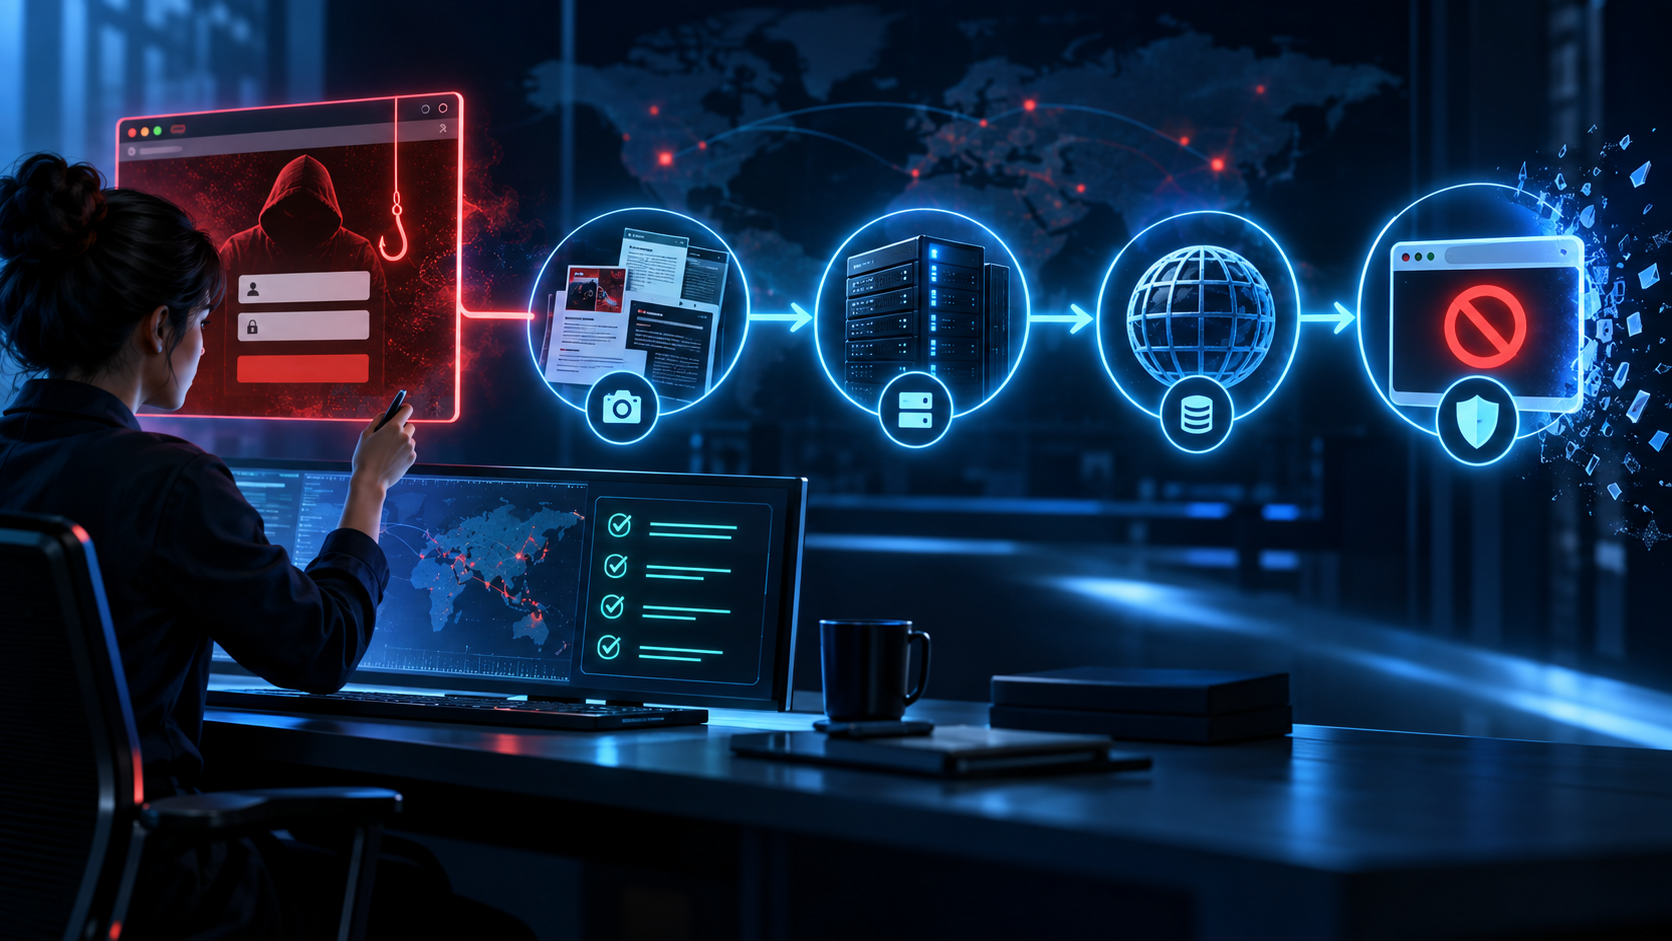
Every venue wants roughly the same case file, so assemble it once: the full URL set, timestamped full-page screenshots showing your brand and the address bar in one frame, the saved HTML, and the registration and DNS records as they stood on the day you filed. The manual takedown process covers how to file each one; this article is about choosing the right door.
Then add what the impersonation venues need and the phishing venues don't: proof that the brand is yours. Australia's Scamwatch tells impersonated businesses to report to the hosting provider, include the impact on their intellectual property rights, and file the report themselves, since the business owns the intellectual property. A missing trademark registration isn't a reason to wait: the USPTO says federal registration is your choice, and the US Copyright Office says your work is under copyright protection the moment it's created and fixed, so the copied text, photos, and code give you grounds for a notice on their own.
Route one: the host, the platform, and whatever sits in front of them
A domain name and the content behind it are controlled by different parties. The registrar sells and manages the name, and the hosting provider runs the server that serves the pages, which makes the host the venue for an impersonation site that isn't phishing. The UK's National Cyber Security Centre warns that takedown requests can take anything between hours to days or even weeks, so the work in the next three sections shouldn't wait for the host to answer.
Finding the host takes a few lookups. ICANN Lookup returns the registrar of record and its abuse contact for a gTLD domain. Resolving the domain to an IP address and mapping that address to its network owner, through an ASN record (the registered number identifying which organization announces that block of addresses) or a reverse DNS query (asking which hostname an address maps back to), gets you to the provider running the server, where RFC 2142 reserves the abuse@ mailbox for this purpose.
Check whether the site has a domain of its own at all. Interisle found that 13% of phishing attacks used resources at subdomain providers, with 89% of those concentrated on just 10 providers. That figure counts phishing attacks, but a clone site on a website builder or a free hosting tier sits in the same position: there's no registrar to write to, and the platform holds both levers.
Expect a content delivery network or reverse proxy in front of the real server, which means the IP address you resolved may belong to an intermediary that never touches the files. Cloudflare's abuse page is the clearest statement of how that works: it doesn't host content for its pass-through services and can't remove what it doesn't host, so it forwards complaints to the website operator and the hosting provider. File with the intermediary anyway; Cloudflare says it responds with details you can follow up on, and that reply may be the quickest way to find out who the origin host is.
Route two: a DMCA notice when someone copied your website
If the site reproduces your pages, a copyright notice under Section 512 of the DMCA is available whether or not the site is phishing, and it doesn't depend on a trademark. The statute lists six elements a notice has to contain: a signature, identification of the copyrighted work, identification of the infringing material and where to find it, your contact information, a good-faith statement, and an accuracy statement under penalty of perjury.
Two limits matter for an impersonation case. The provider's obligation is to act expeditiously to remove, or disable access to, the material, so a DMCA notice removes the copied pages, not the domain, and an operator can keep the name and rebuild with original text. If the operator files a counter-notice, the safe harbor lets the provider restore the material not less than 10, nor more than 14, business days later unless it's been told you've filed suit. Google takes the same notice separately for each of its products, so web search, image results, and ads each need their own filing.
Route three: taking the domain on trademark grounds
This is the section for counsel, because it's the only route that reaches the domain name itself when the site isn't phishing. Under ICANN's Uniform Domain Name Dispute Resolution Policy, which binds every accredited registrar, a complainant has to prove three things: the domain is identical or confusingly similar to a mark in which the complainant has rights, the registrant has no rights or legitimate interests in it, and it was registered and is being used in bad faith. The remedies are limited to cancellation or transfer of the domain, with no damages and no order against the operator.
The timeline is measured in weeks. Under the UDRP Rules, the respondent has 20 days to respond and the panel forwards its decision within 14 days of its appointment, and the venue is busy: WIPO's Arbitration and Mediation Center handled more than 6,200 domain name cases in 2025, its highest caseload on record.
Two alternatives sit alongside it. ICANN describes the Uniform Rapid Suspension System as a lower-cost, faster complement to the UDRP for the most clear-cut cases, on a clear and convincing evidence burden. In the United States, the Anticybersquatting Consumer Protection Act, 15 USC 1125(d), creates civil liability for registering, trafficking in, or using a domain confusingly similar to a distinctive mark with a bad-faith intent to profit, and lets a court order forfeiture, cancellation, or transfer of the name. It's slower and costlier than a UDRP filing, and it's the route that can reach the operator personally.
Registration isn't required for any of these, but it changes the evidence you carry in. The USPTO says a federal registration gives you a legal presumption that you own the mark and rights throughout the entire United States, where unregistered common-law rights are based on use within a particular geographic area. Counsel's questions are which marks are registered and where, whether the goal is the name or the operator, and what the case file needs to look like when a panel sees it.
The campaign around the site
A fake site rarely generates its own traffic. Paid search ads on your brand terms, social accounts, messages carrying the link, and counterfeit listings on marketplaces selling the same goods all point customers at it, and each survives the removal of the page it points to. The listings in particular tend to reappear under new seller accounts once the first set is gone.
Google Ads doesn't allow ads that infringe trademark rights and takes complaints from trademark owners, with two conditions. The complaint is accepted only within the countries and industries where you've demonstrated rights, and an upheld complaint is generally applied on an ongoing basis to ads using the same second-level domain (the registrable name, like example.com) in their final URL. Scamwatch's advice for social platforms has the same shape: if your brand is being used in scam ads, report that activity directly to the platform.
Then there's the rebuild. Interisle found that 37% of phishing domains were registered in bulk, across 70,541 sets at 174 registrars, so an operator who bought a batch of your lookalikes has the next one ready before your first report is answered. Watching new registrations, certificates, and DNS changes through lookalike domain monitoring is how the replacement gets caught during setup and tied back to the case you already opened.
Protect customers while the site is still up
Every venue above runs on someone else's clock, so customer protection has to run on yours. If the site is phishing, report it to Google Safe Browsing, which helps protect over 5 billion devices every day with browser warnings. That's a warning rather than a removal, and it doesn't apply to a counterfeit storefront that isn't collecting credentials.
For the rest, Scamwatch's guidance is to put warnings on your social media accounts, website, app, and at points of sale so customers know what's happening and where to report it. Give the support desk a one-page script listing which domains, phone numbers, and accounts are genuinely yours, and route every customer report into the case.
What to ask a takedown vendor about impersonation sites
Once the volume passes what one person can carry alongside another job, the question becomes what a service actually does with an impersonation case that isn't phishing. Bolster AI's automated takedown flow describes API-based takedown relationships with major hosting platforms, automatic submission of fraudulent URLs with proof of fraud attributes to global blocklists, and post-takedown monitoring for recurrences; it doesn't describe filing UDRP complaints or court actions. Put the same questions to any vendor, Bolster AI included:
- Which venues do they file with for a clone or counterfeit site that has no credential form, and what happens to a case that needs a trademark dispute or counsel?
- Before a request goes out, how do they tell an impersonation from an authorized reseller, a franchise microsite, or a compromised legitimate site?
- What does the second request look like when the host doesn't answer, and who else in the chain can they reach?
- Who handles the ads, accounts, and listings feeding the site, and what do they do to reduce harm while it's still up?
The sequence, in order
- Categorize the site: phishing, cloned website, counterfeit storefront, fake support or partner site, or parked lookalike. Rule out authorized properties and compromised domains.
- Capture the evidence once: URLs, timestamped captures, saved HTML, registration records, DNS records, and proof of your rights in the brand and the content.
- If it's phishing, file with the registrar and the host in parallel, and report the page to Safe Browsing.
- If it isn't, file with the host or the platform on impersonation and intellectual property grounds, and with any CDN in front of it.
- Send a DMCA notice for copied pages, to the host and to each search product separately.
- Have counsel weigh a UDRP or URS filing, or an ACPA action, if the domain itself is the problem.
- File a trademark complaint against search ads, and report scam ads, accounts, and listings to the social platforms and marketplaces carrying them.
- Post customer warnings and brief the support desk.
- Watch registrations, certificates, and DNS for the rebuild, and correlate it to the original case.
Knowing how to take down a fake website comes down to that first decision. A request that sits for a week at the wrong door can move in hours at the right one, and which door is right is something you can settle in the first hour.
Bolster AI detects external threats including phishing sites, lookalike domains, fraudulent social accounts, fake mobile apps, fraudulent ads, and marketplace abuse, connects related infrastructure into a single campaign, and removes them. Detection and takedown run as one workflow rather than as two separate promises, with automation carrying the volume and Bolster AI analysts handling the cases that need judgment.
If you'd rather see this run against the sites currently using your brand than work the venues one at a time, book a demo and bring the last impersonation case that took longer than a week to close.
TL;DR: How you take down a fake website impersonating your brand depends on what the site is doing, not on how much it looks like you. If it harvests logins, card numbers, or one-time codes under your name, it's phishing, and the registrar has a contractual duty under ICANN's 2024 DNS abuse amendments to act on evidence. If it's a cloned website, a counterfeit storefront, or a fake support page with no credential form, the registrar has no such duty, and the routes are the hosting provider on impersonation and intellectual property grounds, the platform if the site sits on a builder, a DMCA notice for copied content, and a UDRP, URS, or ACPA action for the domain itself. Either way, the ads, accounts, listings, and replacement domains around the site need their own reports, and customer warnings go up before the first venue answers.