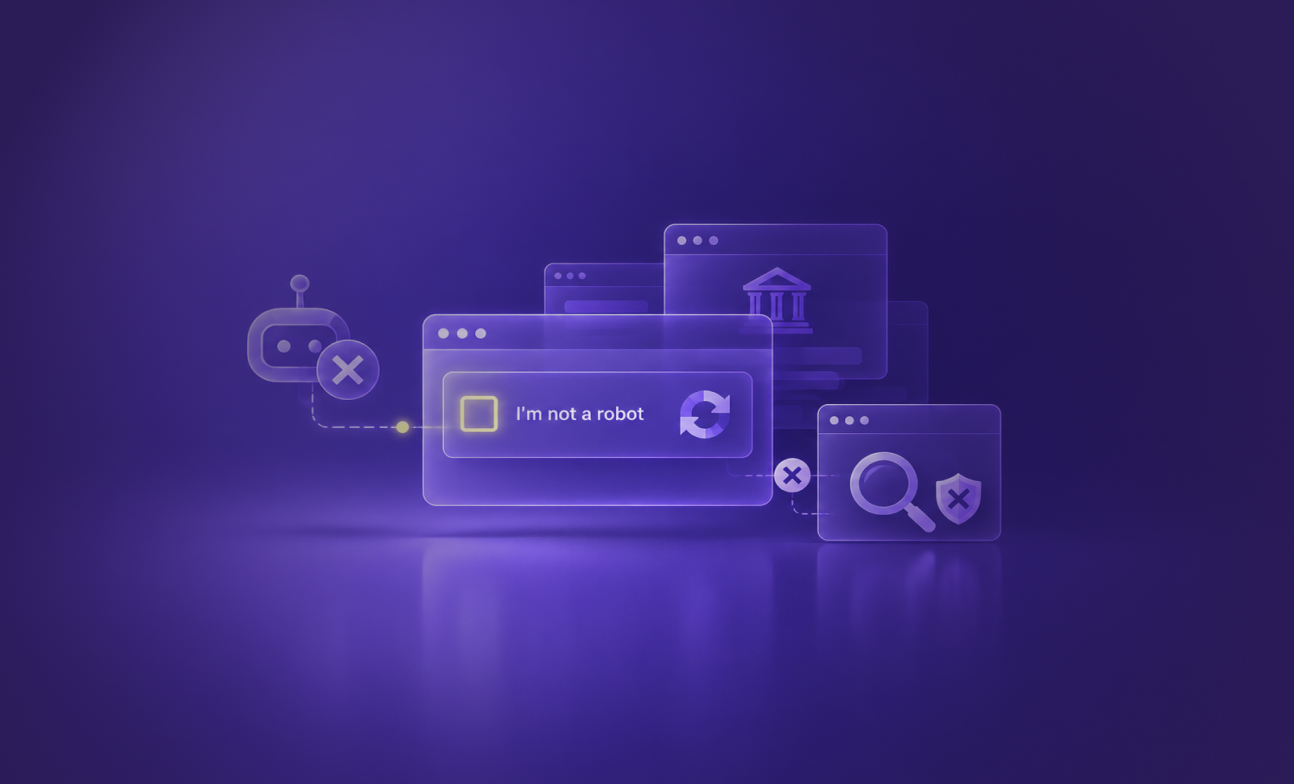
CAPTCHA was designed to keep automated traffic out of legitimate websites. Attackers have flipped that model. Across phishing and scam infrastructure, challenge pages are increasingly used to keep automated security scanners from seeing what sits behind them. Put a CAPTCHA in front of a credential-harvesting page and a scanner may record the challenge instead of the phish. The site can end up classified as unreachable, unknown, or otherwise escape a malicious verdict.
The human victim has a very different experience. They click through the challenge and reach the intended page. Worse, the familiar verification screen may actually make the site feel more legitimate.
At Bolster AI, we encounter and resolve approximately 80,000 to 130,000 challenges every day as part of our production detection pipeline. What we’re seeing at that scale makes one thing clear: challenge gating is no longer an edge-case evasion technique. It has become part of the standard attacker playbook.
Key Findings
- CAPTCHA has become an evasion technique. Attackers use challenge pages to prevent automated security systems from reaching malicious content.
- The tactic is operating at significant scale. Bolster AI resolves approximately 80,000–130,000 challenges every day across the infrastructure we scan.
- Cloudflare-style verification dominates. The majority of challenges we encounter either use legitimate Cloudflare protections or imitate the familiar Cloudflare verification experience.
- Attackers use both legitimate and fake security controls. We see commercial challenge services, spoofed verification pages, and fully custom gates.
- Challenge pages rarely operate alone. Attackers frequently combine them with geographic, network, device, and referrer filtering to control exactly who can see the malicious payload.
- The same gate that blocks scanners can increase victim trust. A familiar security check can make the fraudulent page behind it appear more legitimate.
By the Numbers
| 80K–130K | CAPTCHA challenges resolved per day by the Bolster AI platform |
| 3M+ | Sites analyzed daily across Bolster AI’s domain monitoring infrastructure |
| 1,500+ | Top-level domains represented in that scanning population |
| 3 | Primary forms of challenge gating observed: legitimate services, spoofed pages, and custom-built gates |
How CAPTCHA Became an Evasion Technique
Automated scanning and crawling underpin security detection at scale. Attackers know that.
A challenge page gives them a relatively simple way to exploit it.
When an automated scanner reaches a CAPTCHA or other verification gate and can’t continue, it never sees the content the attacker actually intends to deliver. Depending on how the detection system handles that result, the site may be recorded as unreachable, unclassified, or simply never receive a malicious verdict.
For the attacker, that’s the point.
The intended victim, meanwhile, arrives through the phishing email, malicious ad, text message, or other lure and passes through the verification step. Instead of creating friction, the challenge can reinforce the illusion of legitimacy. People are accustomed to seeing CAPTCHA and security checks on legitimate websites. A verification screen in front of a fake login page can therefore act as both an evasion layer for scanners and a trust signal for victims.
The security mechanism has effectively been inverted.
Three Ways Attackers Deploy Challenge Gates
1. Legitimate services used defensively by attackers
Commercial services such as hCaptcha, reCAPTCHA, and Cloudflare can be deployed directly on malicious infrastructure.
The attacker gets sophisticated anti-automation technology maintained by someone else, often at little or no cost. More importantly, the service is doing exactly what it was built to do: distinguishing automated traffic from human visitors.
The difference is who is being protected.
Instead of protecting a legitimate site from abusive automation, the technology is protecting a malicious site from security infrastructure trying to inspect it.
2. Spoofed verification pages
Other attackers recreate the appearance of well-known verification screens without using the underlying service.
These pages serve two purposes. They create another obstacle for automated analysis while borrowing the credibility of a recognizable security brand.
Bolster AI’s research team has previously documented more than 6,000 fake CAPTCHA pages built around a single trusted brand, many carrying variants of the same “Verify Your Request” language.
That makes the challenge page itself a useful signal. A fake Cloudflare or similar verification screen isn’t merely something standing between a scanner and the payload. It’s a form of impersonation that can indicate malicious intent before the scanner ever reaches the next page.
3. Fully custom gates
The third category is purpose-built.
Attackers create their own puzzles, interaction requirements, redirects, and verification flows specifically to control access to malicious content.
These implementations are less standardized and therefore harder to identify and traverse consistently. That unpredictability is part of their value to the attacker.
A Clean Scan Doesn’t Always Mean a Clean Site
CAPTCHA is often only one layer of the evasion stack.
We regularly see challenge pages combined with conditions based on geography, network origin, device characteristics, browser behavior, and referrer. Challenges can also be chained, forcing a visitor through multiple gates before the malicious content appears.
The goal is not simply to determine whether the visitor is human. It’s to determine whether the visitor looks like the right human.
A phishing campaign targeting consumers in Sweden, for example, might reveal its payload only to a Swedish mobile IP using the expected browser and arriving through a particular referrer. Everyone else gets a challenge page, placeholder, redirect, or benign content.
Our research team observed the same conditional-delivery model while investigating a class of e-commerce impersonation attacks that only rendered fraudulent content to visitors arriving through a paid advertisement on a mobile user agent. Direct browsing returned a placeholder. Automated crawling saw nothing useful.
The underlying problem is one of vantage point.
When the attacker controls what a scanner is permitted to see, a clean result is not evidence of a clean site.
What 80,000-130,000 Daily Challenges Tell Us
These figures come from Bolster AI’s production detection pipeline, not a sampled research environment.
Our domain monitoring infrastructure analyzes more than 3 million sites daily across 1,500-plus top-level domains, and the challenge counts reflect gates encountered and resolved while scanning that population.
The volume isn’t static.
Challenge activity can rise when widely distributed phishing kits include gating by default, effectively turning an evasion technique into an out-of-the-box feature for campaign operators. We also see movement during periods of elevated fraud activity, when attackers are running more infrastructure at once.
That makes challenge prevalence useful threat intelligence in its own right.
Changes in how often gates appear, which verification brands attackers imitate, and which other filtering techniques are paired with them provide signals about how phishing infrastructure and attacker tradecraft are evolving.
How Bolster Gets Behind the Gate
A scanner that stops at the challenge can only classify what the attacker allows it to see.
Bolster AI treats the challenge as a door, not the destination.
Our scanning infrastructure first identifies that a gate is present, including spoofed and custom implementations that may not carry an obvious signature. That’s important because a system has to recognize that it is looking at an access-control layer before it can determine what to do next.
We then traverse the challenge and analyze the content delivered behind it. The malicious determination is made based on the actual destination rather than the benign wrapper presented to the scanner.
Reaching that content takes more than solving a visible puzzle.
Attackers increasingly evaluate the entire request: where the visitor originates, what device and browser they’re using, how they arrived, and whether their behavior resembles the audience the campaign is designed to target.
Our approach accounts for those conditions rather than simply attempting to brute-force a CAPTCHA. The specific mechanics are core detection tradecraft and aren’t something we publish.
The outcome is what matters: challenge-gated infrastructure gets classified based on what the attacker is attempting to conceal.
What This Means for Defenders
Challenge gating creates a structural blind spot for detection systems that can’t get beyond it.
For defenders, that has several implications.
False negatives aren’t distributed evenly. Attackers investing in layered gating are deliberately trying to avoid detection. The infrastructure most difficult for automated systems to inspect may therefore be some of the infrastructure most worth inspecting.
Detection speed affects takedown speed. Bolster AI’s automated takedowns can remove a confirmed malicious site in as little as two minutes, but that clock can only start once the site has been correctly classified. If a challenge prevents detection, it also delays remediation.
“Unknown” deserves scrutiny. A challenge-gated page shouldn’t automatically be treated as benign simply because its destination couldn’t be observed. In an environment where attackers intentionally manufacture that outcome, the inability to inspect a page is itself meaningful.
The gate can be evidence. Spoofed CAPTCHA and verification screens represent a second layer of abuse. The attacker may be impersonating both the ultimate target brand and the security provider whose trust signal is being used to get the victim there.
Most importantly, defenders need to think about visibility differently.
Detection coverage isn’t only a question of how much infrastructure a system scans. It’s also a question of whether the system can see what attackers are actively trying to prevent it from seeing.
The Question to Ask Your Current Tooling
If you’re evaluating detection coverage, don’t just ask how many URLs a platform scans.
Ask what happens when one of those scans hits a wall.
How many challenge-gated pages did the platform encounter last month? How many did it resolve? How many were ultimately classified based on what was actually behind the gate? And how many were left as unknown?
Attackers are increasingly controlling the conditions under which malicious content becomes visible. A detection system that accepts the attacker’s version of the page is only seeing what the attacker wants it to see.
The challenge isn’t the destination. The question is what’s behind it.
Want to see what Bolster AI finds when scanning for threats targeting your brand? Request a demo.