Google says it blocked or removed 415 million ads and suspended more than 5 million accounts in 2024 for violating the policies it associates most closely with scams. The 2025 edition reports over 602 million ads removed under those policies and more than 4 million accounts suspended for scam-related activity. The numbers are enormous, and none of them tells you what got through.
Neither report publishes the total number of ads served, so the removals have no denominator. What they measure is enforcement effort, which is a real thing to measure and a different thing from what your customers were exposed to.
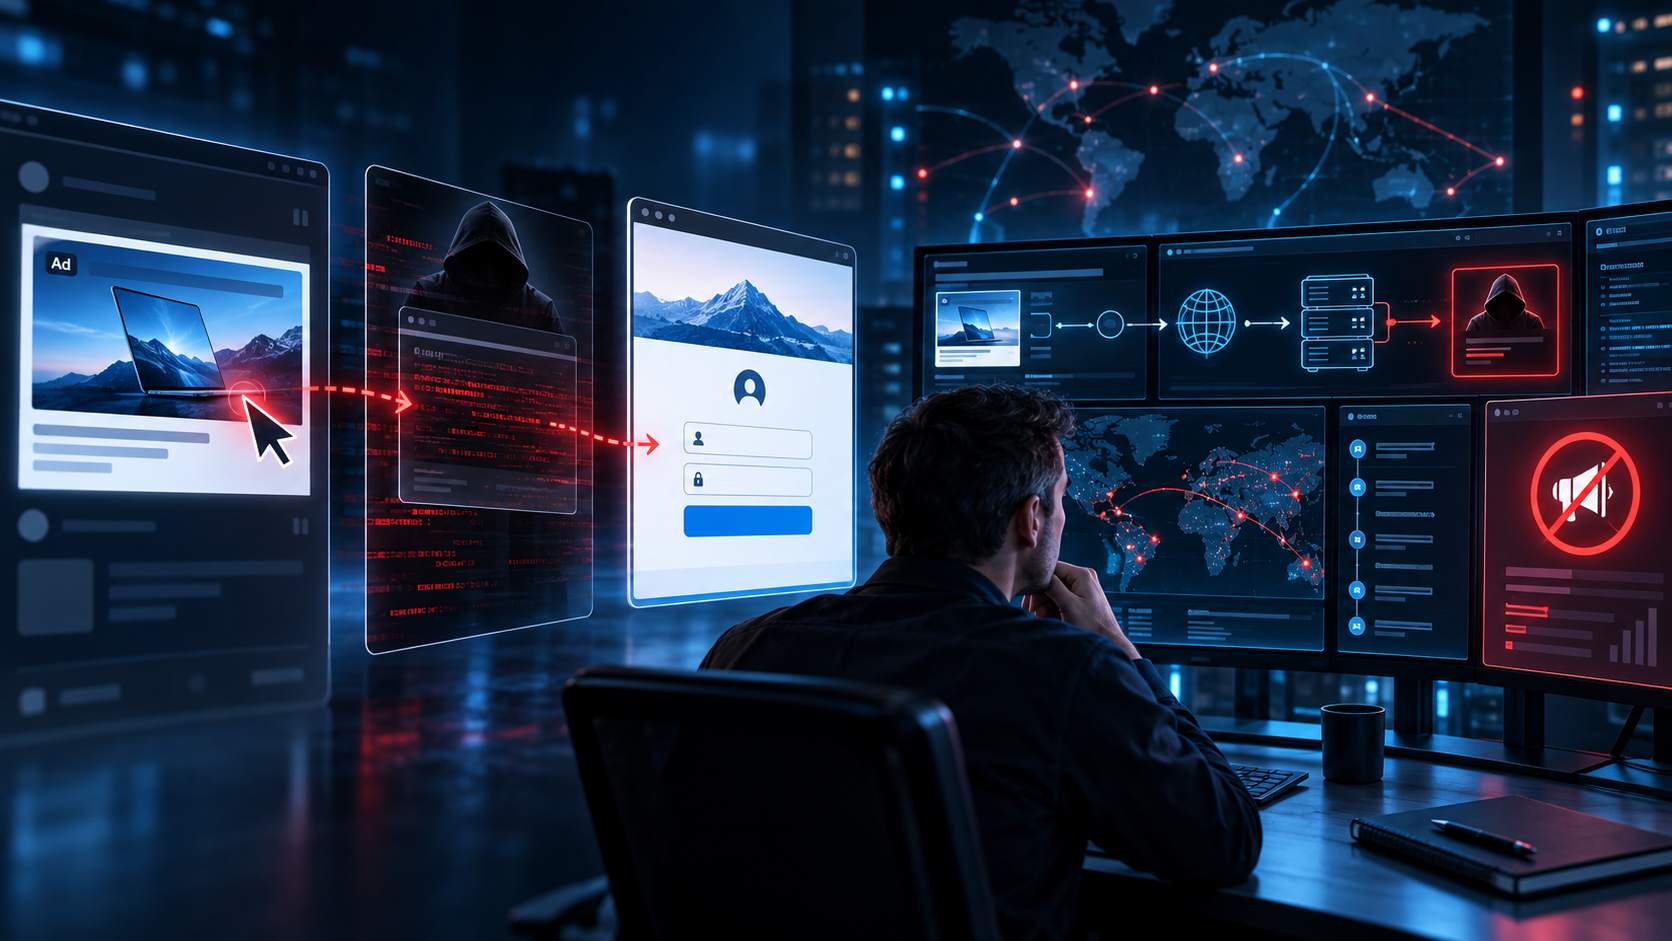
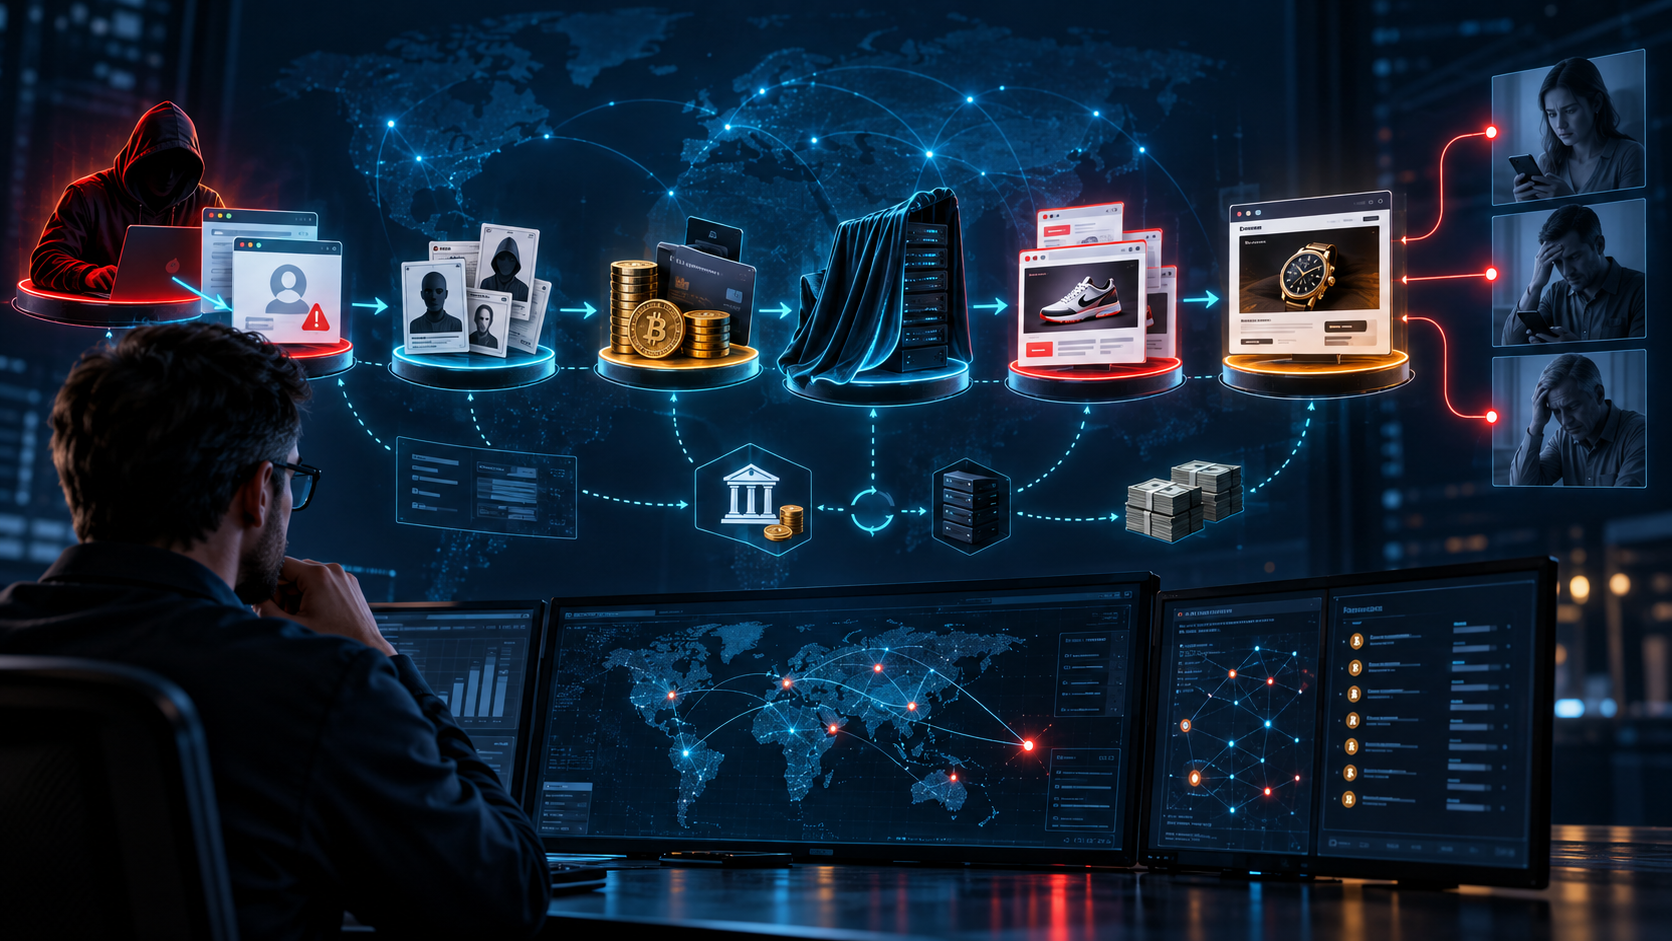
The more useful question is what sits behind an ad before anybody removes it. Someone writes the ad itself, someone supplies the advertiser account, someone attaches a payment method, and someone collects money for the placement. That first piece, the creative, is the only part of the chain a brand ever sees. Follow the order and scam ads stop looking like content that slipped past a filter and start looking like a distribution channel with suppliers, prices, and replacement stock.
What a scam ad is, and what it isn't
A scam ad is a paid placement bought through the same self-service tools a small business uses to promote a storefront, and its job is to move the viewer into a fraudulent purchase, a credential page, or a conversation with someone working from a script. Nothing in the delivery path is broken, hidden, or technically exotic. The buy itself is ordinary, which is what makes the category awkward for defenders trained to look for something that failed.
Two neighboring terms get mixed into this and shouldn't be. Ad fraud is value stolen from the advertiser through invented impressions and automated clicks, so the victim is a marketing budget. Malvertising uses an ad to deliver malware to a device. Scam ads go straight at the audience, and the money moves because a person decided to hand it over.
The operations behind scam ads are well funded
Start with what the buying produces. The FTC put reported losses to scams that started on social media at $2.1 billion in 2025, about eight times the $261 million reported in 2020, and found that more than 40% of people who lost money to a scam on social media said it started when they ordered something they'd seen in an ad. Read that second denominator carefully: it counts the people who reported losing money to a social media scam, not everyone who reported fraud.
Investment fraud is where the largest sums sit. The FBI's Internet Crime Complaint Center recorded $7.2 billion in reported losses to cryptocurrency investment fraud in 2025, the highest source of financial losses to Americans that year, and lists advertisements alongside text messages, social sites, and dating applications as routes these operations use for first contact. The bureau attributes much of that activity to organized criminal enterprises based in Southeast Asia that use trafficking victims as forced labor to run the operations.
Operations of that size can afford a media budget. In October 2025 the Justice Department indicted the chairman of the Prince Group over Cambodian forced-labor scam compounds and sought forfeiture of about 127,271 bitcoin, then worth roughly $15 billion. The charges are allegations, the case hasn't been decided, and the filing says nothing about advertising. What it does show is the order of magnitude of capital that concentrates in one operation, which is the relevant figure when you're wondering who can afford to buy placements continuously.
Where the advertiser accounts come from
An advertiser account with spending history and a clean record is worth more than any creative that runs through it, and there are three ordinary ways to get one. Theft is the first. Google's guidance for owners of compromised Google Ads accounts tells them to collect timestamps showing unauthorized user additions and evidence of budget increases that deviate from historical management, which is a fair description of what an intruder does with somebody else's marketing budget.
Rental is the second, and the platforms document it themselves. In February 2026, Meta sent cease and desist letters to eight of its former Business Partners over services that included phony un-ban or account restoration offers and renting access to trusted accounts that helped clients evade enforcement. An account with years of history behind it doesn't read as a first-time buyer to any review system, and that is precisely what the renter is paying for.
The third route needs neither theft nor an intermediary. Accounts get opened faster than the platform closes them, and verification is the countermeasure aimed at that. Google asks advertisers for personal information, a government-issued photo ID, and answers about their organization, products, ads, and relationships with other organizations, and pauses accounts that miss the deadline. Meta said in March 2026 that verified advertisers drive 70% of its ads revenue, with a target of 90% by the end of 2026, which is also a platform saying how much of its ads revenue still arrives from advertisers it hasn't verified.
Cloaking is a product, and it has a price list
Getting an account is one job. Getting past review is a separate one, and it has its own supply. The technique at the center of it is cloaking, which means showing the review system one page while showing the person who clicks a different one. Meta calls it a technique that impairs ad review systems by concealing the true nature of a website linked to an ad, and Google's policy defines it as showing different content to different people, or to Google, to hide things that might break the rules.
None of this is improvised, and it hasn't been for a long time. Researchers at Google and North Carolina State University who bought and analyzed cloaking software in 2016 found 10 packages priced from $167 to $13,188, sold the way commercial software is sold. The approach has lasted because it defeats the cheapest step in review, which is looking at the page.
For anyone who owns a brand, the practical consequence is uncomfortable. The destination your customer reached and the destination the platform reviewed may never have been the same page, so what a customer sends you afterward can be the only surviving record of where the ad actually led.
The money arrives before the correction does
Money and judgment arrive in an order that favors the buyer. Whoever bought the placement pays up front, using whatever payment instrument came attached to the account, and the platform is paid before anyone has judged the campaign. A buy that clears review starts spending immediately. For anything review misses, the correction lands afterward, when detection, a user report, or a second look catches a placement that's already running.
Meta and Google both publish proactive numbers, and both are worth reading closely. Meta says it removed more than 159 million scam ads in 2025, 92% of them before anyone reported them. Google says it blocked or removed 8.3 billion ads in 2025 and stopped over 99% of them before they were ever seen by anyone. Each percentage is a share of what the platform caught, not a share of what ran.
That's why a transparency report can't answer the question a brand actually has. It describes how much the enforcement machinery caught and how quickly, and it leaves out how much inventory was bought, how long a typical placement ran, and how many people it reached before it came down.
Why one removal rarely ends the campaign
The clearest published description of what happens after enforcement lands is Google's circumvention policy, which reads as a list of behaviors common enough to prohibit by name: creating variations of ads, domains, or content that have been disapproved, opening new accounts after a suspension to re-enter the system, and using click trackers to redirect people to prohibited destinations. Every item there is a way to keep a campaign running after a creative comes down.
Google's penalty for it says something about how routine the behavior is. Accounts caught circumventing enforcement are suspended on detection, without prior warning, and barred from advertising again, which is the treatment reserved for conduct a warning wouldn't change.
Redeployment happens on the landing side too. In the 2020 USENIX Security study of phishing at scale, when researchers reported the most sophisticated campaigns by hand, attackers redeployed subsequent attacks on different subdomains or paths once the original addresses reached the systems that block them. The kit stays where it is, the address moves, and the ad points somewhere new.
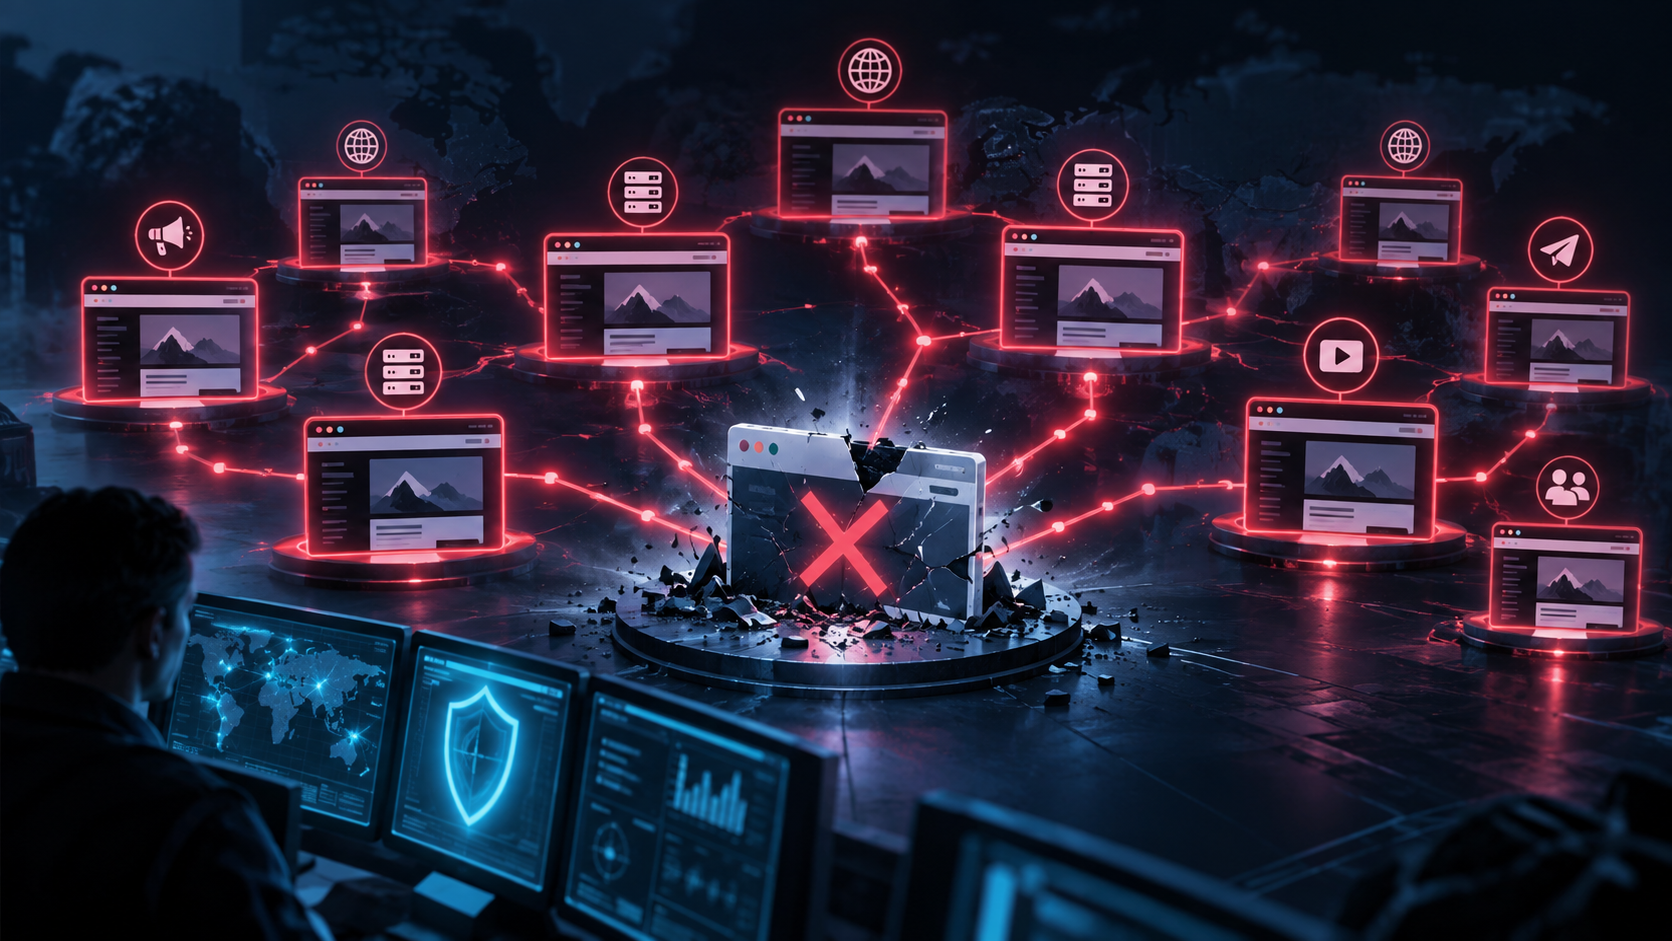
Pulling a creative retires the cheapest asset in the operation. If the account wasn't suspended alongside the ad it keeps working, the payment instrument and the audience definition go untouched, and the landing page sits with a host the ad platform has no authority over.
What this changes for brand and security teams
Domain monitoring finds the landing page when the operator registers a lookalike domain for it. It doesn't find the ad. The placement leaves no registration to catch, and the destination can sit behind a link shortener, a redirect through a host nobody would flag, or a domain bought years earlier. That puts paid surfaces on the list in their own right, which means monitoring for fraudulent ads that impersonate a brand alongside the landing infrastructure sitting behind the creative.
The pieces also belong to each other. An ad, the page behind it, the fraudulent social accounts and scam posts amplifying it, and the account that bought the placement are components of one campaign, and the acquisition funnel behind a scam is what a program defends against rather than any single artifact inside it.
Evidence carries a deadline the rest of the work doesn't. The creative disappears when the campaign's run ends or the platform acts, whichever comes first, so capture happens while the placement is live or not at all: the creative, the advertiser name shown on it, the full redirect chain, and the hosting and registration behind the destination. Automated takedowns run on evidence packages of that kind, and it's a fair question to put to any vendor, Bolster AI included: what do they capture before an ad disappears, which platform portals do they submit to, and what do they watch for once the creative is down?
Questions worth putting on the table
This problem falls between two teams. Marketing sees an advertising issue, security sees an alert with no asset it recognizes, and the customer sees your logo on something that took their money. Five questions surface the gap faster than an audit does:
- Who owns paid placements as a threat surface, and where does a customer's screenshot of a scam ad go when it arrives?
- What did our last complaint to a platform actually contain, and did anyone check whether the account behind the ad came back under a new name?
- How would we find out that an ad impersonating us ran at all, if nobody inside the company sat in the target audience?
- What gets captured while a placement is still live, who keeps it, and would it hold up if the case reached a registrar or counsel?
- When a vendor says a campaign is finished, what have they been watching, and for how long after the ad came down?
None of those has one correct answer, and the answers change what's worth measuring. A team that counts removed ads will report its best year in the year attackers bought the most inventory. A team that can say how fast a campaign came back, and under what name, is measuring something the operator on the other side cares about.
Bolster AI detects external threats including phishing sites, lookalike domains, fraudulent social accounts, fake mobile apps, fraudulent ads, and marketplace abuse, connects related infrastructure into a single campaign, and removes them. Detection and takedown run as one workflow rather than as two separate promises, with automation carrying the volume and Bolster AI analysts handling the cases that need judgment.
If you'd rather put those five questions to a live platform than to a capability matrix, book a demo and bring the last scam ad a customer sent you that nobody could trace.
TL;DR: Scam ads are bought through the same self-service systems legitimate advertisers use, which makes the supply chain behind them more interesting than the creative. The advertiser accounts come from three places: compromised accounts, established accounts rented out by intermediaries, and new accounts opened faster than verification closes them. Platforms collect the money at the point of sale and enforce afterward, so the removal counts in their transparency reports measure enforcement effort against a total those reports never publish. Taking one creative down leaves the account, the payment method, the audience definition, and the landing infrastructure intact, which is why the same operation reappears under a different name.