There is a category of closed tickets I have learned to distrust, and it is the brand impersonation case that ends with a confirmed removal and nothing else attached to it. The page is gone, the evidence is archived, the alert queue is one item shorter, and the operation behind that page has lost almost nothing it actually valued. When the same lure reappears a week later on different hosting, the instinct inside most security and fraud teams is to look for the failure in their own process, usually in speed or in the wording of the notice. That instinct is mostly misplaced, because recurrence is the predictable output of an enforcement model aimed at the cheapest and most replaceable part of an attack campaign.
The more productive question is not why the fake site came back, but which parts of the campaign never went anywhere in the first place. Answering that means being precise about what a takedown removes, what it leaves standing, what the notice itself teaches the operator on the other side, and which metrics quietly declare victory while the threat surface is still occupied.
What a Takedown Actually Removes
It helps to be exact about the mechanism, because the word takedown carries more authority than the process does. As the practitioner guidance in Takedown 101 describes it, a takedown request is an extrajudicial process, a report to an operator of internet infrastructure or a digital platform asking them to act on content they are hosting. Nothing about that is a legal ruling against the person running the campaign, and nothing about it obliges the operator to reach a particular conclusion. What you are doing is persuading a third party that content on their estate violates their own terms, which is why the same report can succeed with one provider and stall with another. The upside of that model is reach, since abuse reports can travel across jurisdictions through platform agreements even where local law does not specifically cover the scam you found.
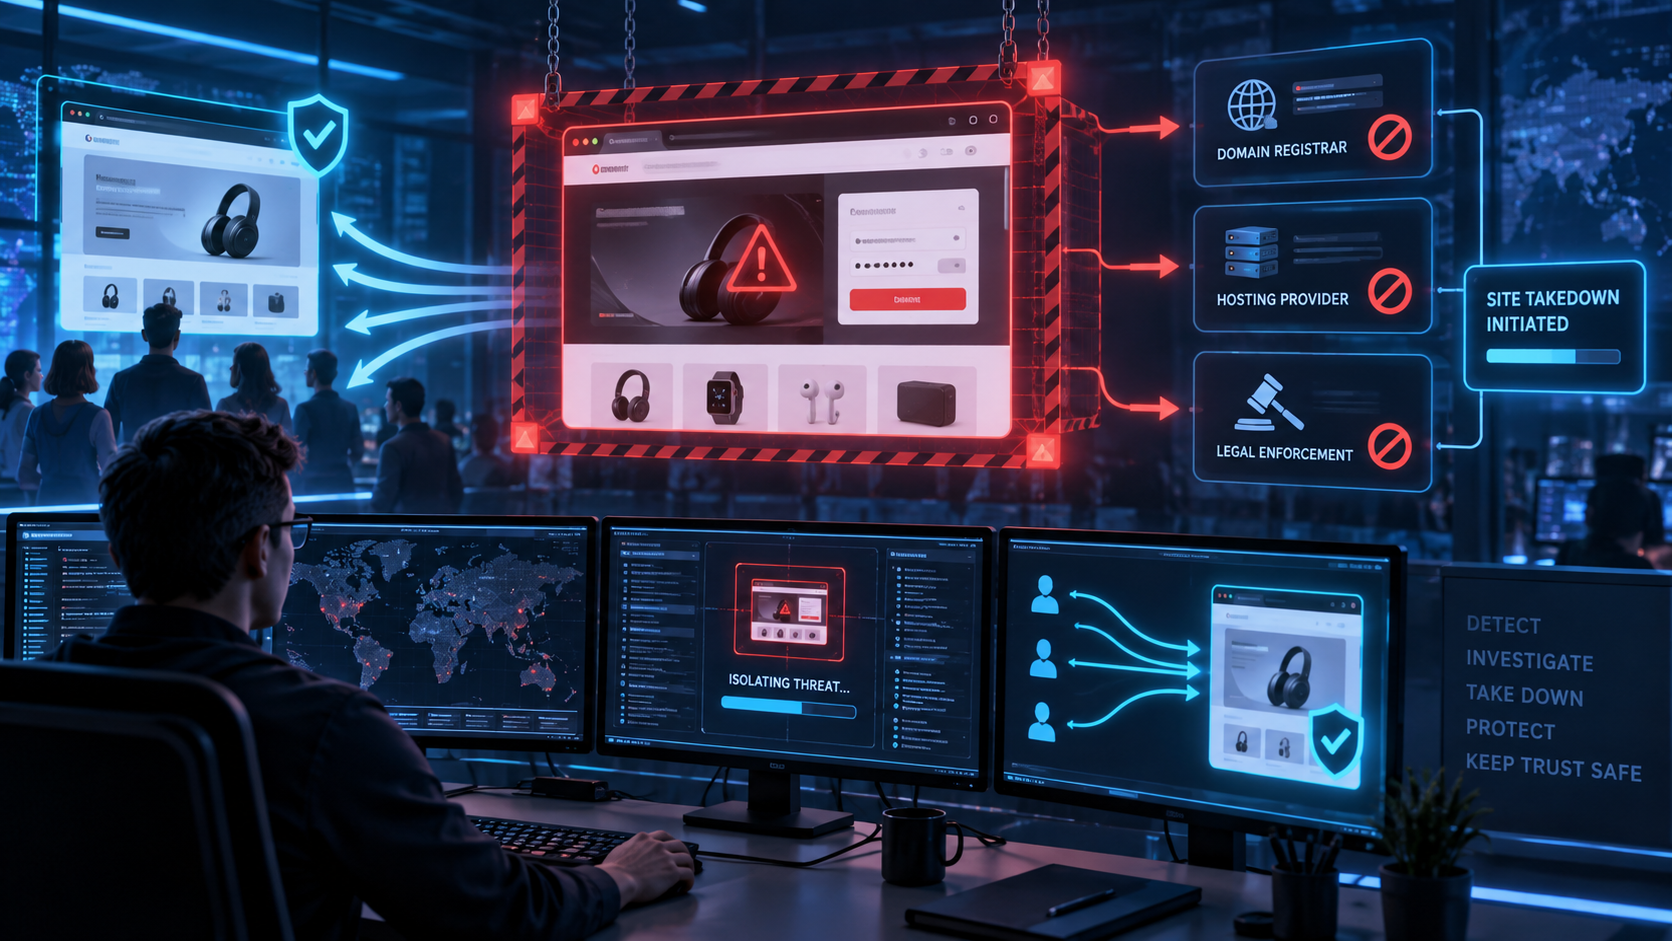
The limitation is what sits inside the scope of a successful removal. You have removed one artifact at one location, usually a page, a profile, or a DNS record, and the phishing kit, the harvested data, the mailing infrastructure, the ad accounts, and the operator all continue unaffected. Doppel's analysis of impersonation enforcement notes that most teams think in terms of a single report per URL, and single-URL thinking is exactly what produces a closed ticket with an intact campaign behind it.
The Attacker's Operational Logic Behind Recurrence
Recurrence looks like persistence from the defending side, but from the attacking side it is simply a deployment schedule. Research cited by Memcyco puts the average phishing site lifespan at 54 hours with a median of just 5.46 hours, which means a significant share of these sites are built to burn fast and disappear before any takedown request clears. Allure Security reports the same shape from a different angle, finding that phishing sites average less than 24 hours of activity before detection or abandonment, with victim engagement concentrated in the first hours of life. Put those together, and the operational reality becomes uncomfortable, because the median site is finished collecting before most detection pipelines have escalated it to enforcement.
An operator working on that clock has no reason to defend any individual site, and every reason to treat removal as an expected end state rather than a setback. The kit is templated, the hosting is disposable, the domain is cheap, and redeployment costs a fraction of what your enforcement cycle costs to run. That asymmetry is why the same brand assets resurface repeatedly with small variations in the domain string, the landing path, or the hosting provider. The consumer exposure sitting underneath that cycle is not small either, with Allure Security citing FTC figures of $2.95 billion in impersonation scam losses in 2024, and every additional hour a fraudulent site stays reachable extending the window in which someone gets compromised.
Structural Reasons the Takedown Window Stays Open
The window stays open because the sequence that closes it is reactive by construction. Memcyco's assessment of the category is blunt on this point, observing that every major brand monitoring and takedown service runs on the same fundamental loop, which is to crawl, detect something that already exists, report it, and then wait for someone else to act. Each of those four stages has its own latency, and only the last one is genuinely outside your control. Compressing the loop is worth doing, but it does not change the underlying arithmetic, because as the same analysis argues, cutting the window from 54 hours to 12 hours still requires the attack to have launched and customers to already be at risk before any protective action becomes possible.
Then there is the variance in the waiting stage, which teams consistently underestimate when they plan capacity. A DMCA notice filed with a responsive host can remove a site within a day, and that best case is what gets quoted in service conversations. The Takedown 101 guidance also notes that response times can stretch by weeks when the host is unresponsive, or the site owner files a counter-notice, and a multi-week tail on a single case is not a rare event across a large portfolio. Meanwhile, the campaign is not waiting for your case to resolve, so the practical exposure is not one window per incident but overlapping windows across every instance in flight.
How Distribution Channels Outlive the Destination
A fake site is a destination, and destinations only matter to the extent that traffic reaches them. That traffic arrives through systems you did not touch when you filed against the hosting provider, which is the most common reason a campaign appears to regenerate instantly. Sponsored search results can route users directly into phishing infrastructure, and stopping that flow requires reporting the advertisement to the ad network and the search platform as separate actions from the site takedown itself. If the ad account survives, the operator swaps the landing page, and the same paid channel keeps delivering the same audience to a new URL within hours.
The same logic applies to every other referral path feeding the campaign, including social posts, messaging distribution, and email lures already sitting in inboxes that no host-level removal can recall. This is why practitioner playbooks treat closing and watching for repeats as a formal step rather than an optional courtesy, since recurrence is anticipated in the workflow design. Doppel frames the discipline well by arguing that effective enforcement combines fast submission through the best-enforced channel with a re-entry plan created the moment the first report is filed. If you enumerate the distribution layer during investigation rather than after the reappearance, the second instance stops being a surprise and becomes a case you already have infrastructure indicators for.
Why the Takedown Notice Can Signal the Attacker to Pivot
Every notice you file is also information you release, because it reaches a third party who will usually contact the account holder before or while acting. From the operator's perspective, a suspension, a warning email, or a request for clarification reveals which layer of their setup you found and which layers you apparently did not. A sequential enforcement approach makes that signal even clearer, since filing against the host first and the registrar later tells the operator exactly how much time they have to migrate the domain somewhere more tolerant. That is the practical case for the guidance in Takedown 101 that reports should ideally be sent to all providers at the same time, so the campaign is disrupted if any one of them acts.
Rejection carries the same lesson in reverse and is arguably more valuable to the attacker. A DMCA filing usually forces a clearer, checklist-driven review than a generic abuse report, but Doppel is careful to note that it is not a guarantee of removal. When a report fails on scope or on the wrong theory, the operator learns that their current configuration survives contact with your enforcement process, and the rational response is to replicate that configuration rather than abandon it. Filing without a re-entry plan therefore converts your own enforcement activity into free reconnaissance for the campaign.
The Wrong Legal Theory Extends the Exposure Window
The theory you assert determines which review queue your report enters and which checklist the reviewer applies to it. Impersonation cases rarely sit cleanly in one category, since a single fake site can mix copied creative assets, unauthorized use of a mark, and purely behavioral fraud that no intellectual property claim describes. Doppel's guidance on this is direct: Do not force copyright logic onto a case that is purely trademark or behavioral, because doing so increases rejection risk and slows the next report you file. That second consequence is the one that extends exposure, as a rejected filing does not simply fail in isolation but consumes days and can reduce the credibility of your subsequent submissions through the same channel.
The corollary is that theory selection should be a channel-level tactical decision rather than a matter of house style. Some platforms respond faster to a copyright claim on the creative used in an advertisement than to a generic report of fraud, which means the copyright route is sometimes the fastest path even when fraud is the real harm. The operational habit worth building is to identify, for each surface in the campaign, which violation type that surface actually enforces well, then file accordingly across all of them at once. Teams that pick one theory and apply it everywhere tend to spend their fastest hours in the slowest queue available.
Platform Enforcement Inconsistency as a Structural Re-entry Point
Because takedowns depend on private terms of service rather than a uniform standard, identical evidence produces genuinely different outcomes across providers. One host removes a page within hours of a structured notice, another requires escalation, and a third accepts a counter-notice and restores the content while your case sits open. Even the more formal route offers no certainty, since a DMCA filing forces a checklist-driven review without guaranteeing removal at the end of it. Add the fact that ad networks and search platforms run entirely separate processes from hosts and registrars, and the enforcement landscape starts to look less like a wall and more like a fence with known gaps.
Operators map those gaps as a matter of routine, because their cost of testing is a single cheap deployment. Once they identify which registrar, hosting provider, or ad surface enforces loosely against your brand, that surface becomes their default re-entry point, and recurrence concentrates there rather than distributing randomly. This is why watching for repeats belongs in the workflow as a named step with an owner and a monitoring window attached, and why the re-entry plan should be written when the first report goes out rather than after the second instance appears. Inconsistent enforcement is not a temporary condition you can wait out, so it needs to be treated as a permanent feature of the threat surface.
Harm That Persists After the Fake Site Is Removed
Removal ends the collection, but it does not reverse anything that was collected while the site was reachable. Memcyco puts this plainly in noting that every account compromised during the exposure window remains at risk once the fake page is gone, since credentials, session tokens, and personal data retain their value independently of the infrastructure that captured them. Where session material was harvested rather than passwords alone, the compromise can persist through a password reset, which means the incident continues inside your own environment long after the external case is closed. Victim engagement concentrates in the first hours of a site's life, so the majority of the damage in a typical case is already done at the moment enforcement succeeds.
This is the gap that makes takedown-only programs feel simultaneously busy and ineffective to the people who fund them. The structural point Memcyco makes is that preemption means intervening before a customer enters a single credential on a fake site, not after that site has been live for 48 hours, and no reduction in response time turns a reactive process into a preventive one. For security and fraud leaders, the practical implication is that external enforcement has to be wired into internal response, covering credential invalidation, session revocation, monitoring of affected accounts, and customer communication. A closed takedown ticket is the beginning of remediation rather than the end of the incident.
Reuse Signals and the Metric That Declares Victory Too Early
Most programs are measured on time to takedown, which is a real operational metric and a poor measure of whether the impersonation problem is shrinking. It rewards closing individual URLs quickly while saying nothing about whether the same operator returned, which surface they returned through, or how much customer exposure accumulated before detection. Doppel identifies the alternative discipline clearly, arguing that if you capture reuse signals you can hunt for the next instance before customers report it, which reframes enforcement as intelligence collection rather than cleanup. The signals worth capturing are the ones an operator cannot cheaply change, including kit artifacts, page structure and asset hashes, registration and hosting patterns, redirect chains, and the specific ad or social accounts used for distribution.
None of that gets recorded if the case closes with a screenshot and a confirmation email, which is what single-URL reporting habits tend to produce at scale. Avoiding the whack-a-mole cycle appears as an explicit strategic priority in takedown playbooks precisely because the default workflow drives teams toward it. A more honest measurement set tracks recurrence per campaign rather than per URL, the proportion of new instances found by monitoring versus reported by customers, the time between removal and reappearance, and the number of distribution channels neutralized alongside each destination. Those numbers move slowly, but they describe whether the operation targeting your brand is becoming more expensive to run.
What Changes the Recurrence Rate
What consistently reduces recurrence is not a faster version of the same loop but a wider one, executed with the campaign rather than the URL as the unit of work. That means treating detection, investigation, enforcement, and post-takedown monitoring as one continuous workflow, so evidence gathered during investigation is still being used weeks after the first removal, and the specific practices that change outcomes are unglamorous and mostly procedural.
- File to every relevant provider simultaneously, so the campaign is disrupted if any one of them acts, and so sequential filing does not telegraph your next move.
- Match the violation theory to what each surface actually enforces, including copyright on ad creative where that route clears faster than a fraud report.
- Report advertisements to the ad network and search platform as actions separate from the site takedown, so paid distribution dies with the destination.
- Write the re-entry plan at the moment the first report is filed, with named reuse signals to monitor and an owner for repeats.
- Connect external enforcement to internal remediation for credentials, sessions, and affected customer accounts compromised during the exposure window.
The realistic goal is not the elimination of impersonation, since abuse reporting remains an extrajudicial request to third parties whose enforcement will never be uniform. The goal is to raise the cost of the second instance and every instance after it, until redeployment stops being cheaper than moving on to a less defended brand. Programs that get there do so by refusing to let a confirmed removal count as a finished case, and by measuring recurrence honestly enough to see where the campaign keeps finding a way back in. If you want to see what detection through takedown looks like as a single operational workflow across domains, social platforms, apps, and marketplaces, request a demo from Bolster.
TL;DR: Takedowns remove a single fake page but leave the underlying campaign infrastructure untouched, so recurrence is predictable until enforcement shifts focus from individual URLs to the operators, hosting patterns, and reuse mechanisms that make impersonation attacks cheap to rebuild.