What is Telegram carding?
Telegram carding is the unauthorized use of stolen credit card information to make fraudulent purchases through Telegram channels, groups, and bots.
Participants in these organized communities share methods, tools, and stolen card details to facilitate illicit transactions.
The activity relies on stolen data obtained from data breaches, phishing attacks, and dark web sources.
According to the 2024 Identity Theft Resource Center report, there were 2,654 reported data breaches affecting over 3.2 billion records in the United States alone, with financial services and retail sectors accounting for 45% of breaches.
How does Telegram carding work?
Telegram carding operations follow a structured four-step process. Fraudsters:
- Obtain stolen credit card details and stealer logs from dark web forums and data dumps.
- Join exclusive Telegram channels and groups (often requiring crypto verification or fee payment).
- Learn and share carding methods, scam scripts, and social engineering tactics within these channels.
- Use specialized tools, BIN lists, and bots to execute fraudulent transactions.
Research shows that 28.1% of links shared in cybercriminal Telegram channels contain phishing attacks, and 38% of executable files contain malware.
The process is highly organized, with members sharing tutorials on Telegram fraud techniques including online store purchases, subscription service access, crypto conversion, and gift card fraud.
Key terms & definitions
BIN (Bank Identification Number): The first four to six digits of a credit card that identify the issuing bank; used by carders to target specific card types.
Non-VBV cards: Credit cards that lack “Verified by Visa” protection, making them easier to use fraudulently without additional authentication.
Drop address: A physical location where stolen goods are delivered, allowing carders to receive purchases without revealing their actual identity.
Carding bot: Automated software tools that streamline parts of the carding process, such as testing card validity or processing transactions.
Phishing: Fraudulent attempts to obtain sensitive information by impersonating legitimate entities, commonly used to steal credit card data.
Popular Telegram carding methods
The four primary carding methods observed by threat intelligence analysts are: online store carding (purchasing goods from retailers with weak security), service carding (unauthorized access to subscription platforms like Netflix and Spotify), crypto carding (converting stolen cards to Bitcoin and digital currencies), and gift card carding (purchasing gift cards for resale or liquidation).
Each method exploits system vulnerabilities and offers varying levels of anonymity. For example, online store carding targets weak security sites using fake IPs and drop addresses, while crypto carding appeals to cybercriminals because digital assets are difficult to trace.
| Carding Method | Description | Key Characteristics |
|---|---|---|
| Online Store Carding | Using stolen credit cards to purchase goods from online retailers | Targets weak security sites; uses fake IPs/VPNs; employs drop addresses for delivery |
| Service Carding | Unauthorized access to subscription services (Netflix, Spotify, Amazon Prime) | Uses non-VBV cards; creates illegal revenue stream by reselling account access |
| Cryptocurrency Carding | Converting stolen card information into digital currencies like Bitcoin | Offers anonymity; uses exchanges with minimal verification requirements |
| Gift Card Carding | Purchasing gift cards with stolen credit card information | Easy to liquidate; less suspicious than direct purchases; difficult to trace |
Online store carding
Online store carding is one of the most common methods discussed in Telegram carding groups, involving stolen credit card details to buy retail goods.
Threat actors target e-commerce apps and sites that have weak defense mechanisms or lack stringent verification processes.
They use VPNs and fake IPs to mask location data, reducing detection risks for their criminal activity.
Some carders also use drop addresses, which are locations where purchased goods are delivered without exposing their real identity.
Dark web monitoring and threat intelligence help organizations spot exposed customer credentials sooner. Request a demo today to see how Bolster AI helps security teams detect and remove digital threats.
Service carding
Service carding focuses on gaining unauthorized access to subscription-based services, streaming apps, and digital platforms. By using stolen credit card details, fraudsters set up accounts without paying.
This method allows threat actors to resell account access at lower prices across Telegram channels, creating an illegal revenue stream. They often use non-VBV cards to bypass authentication checks and avoid detection.
Cryptocurrency carding
Crypto carding is popular among cybercriminals because digital currencies offer a degree of anonymity, making transactions difficult for authorities to trace.
Carders exploit crypto exchanges and wallets with minimal verification, reducing exposure and prosecution risks.
Gift Card Carding
Gift card carding involves purchasing gift certificates using stolen card details. These cards are then sold or used to buy goods, serving as an easy liquidation method for threat actors.
Some carders specialize in buying gift cards from retailers offering promotions, maximizing illicit profits while maintaining high anonymity.
Learn more about why scams and cybercrime flourish on Telegram.
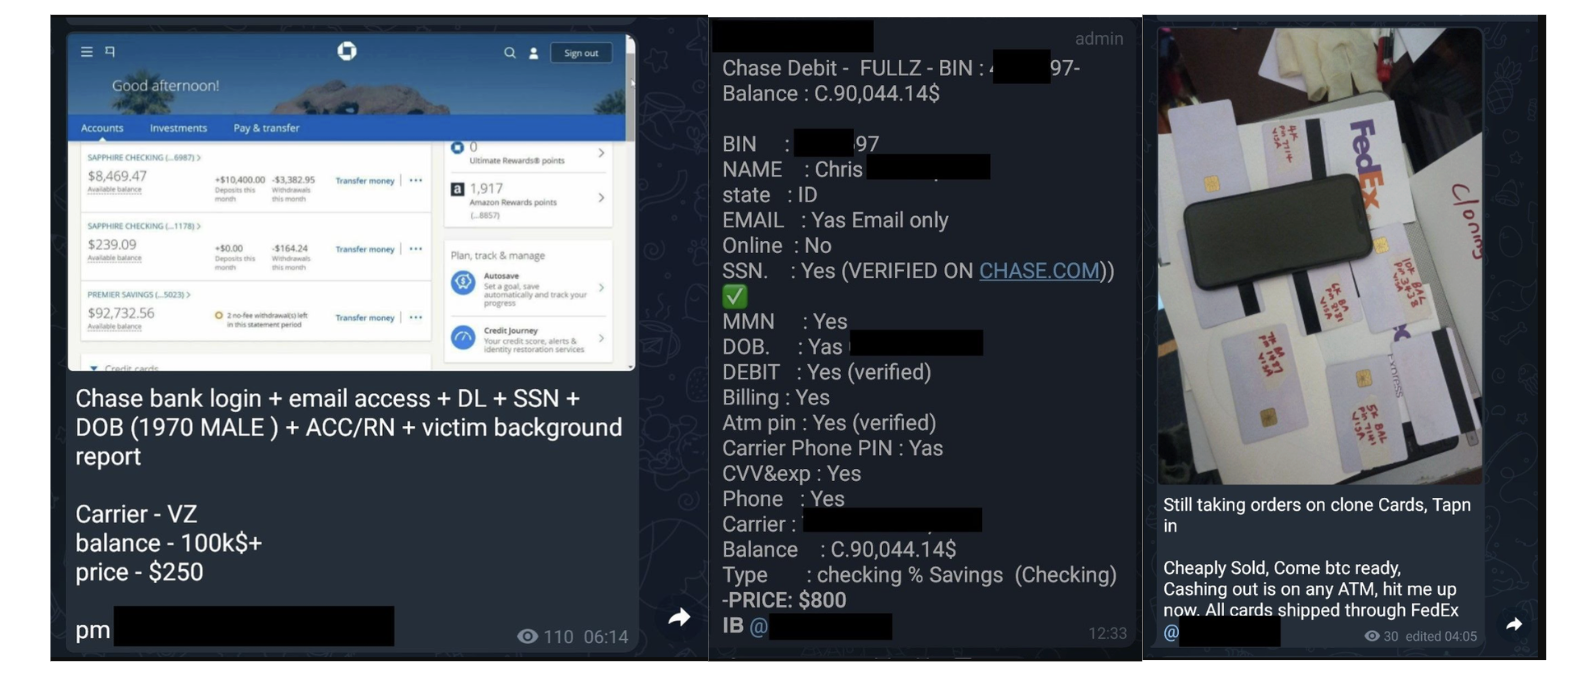
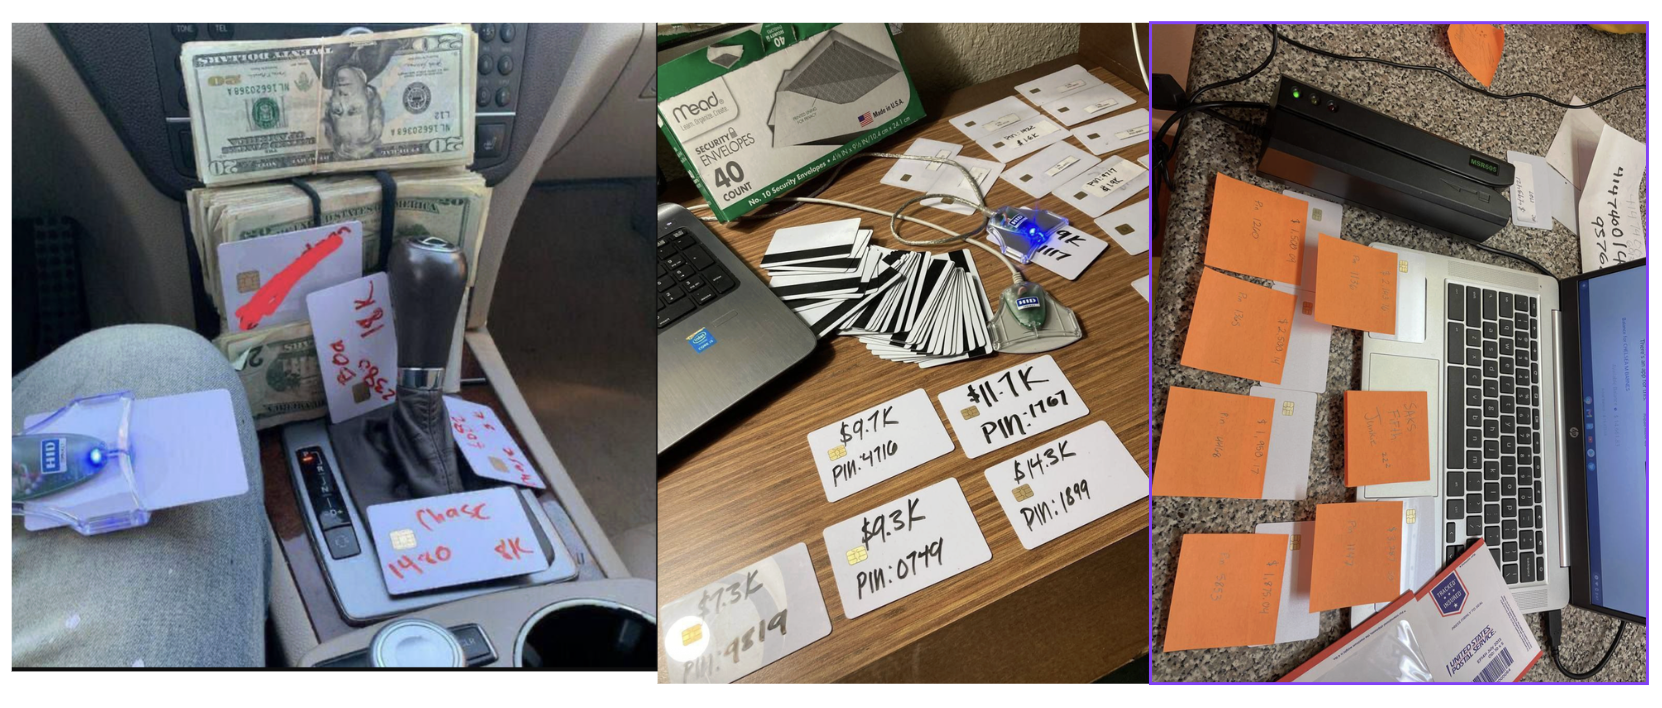
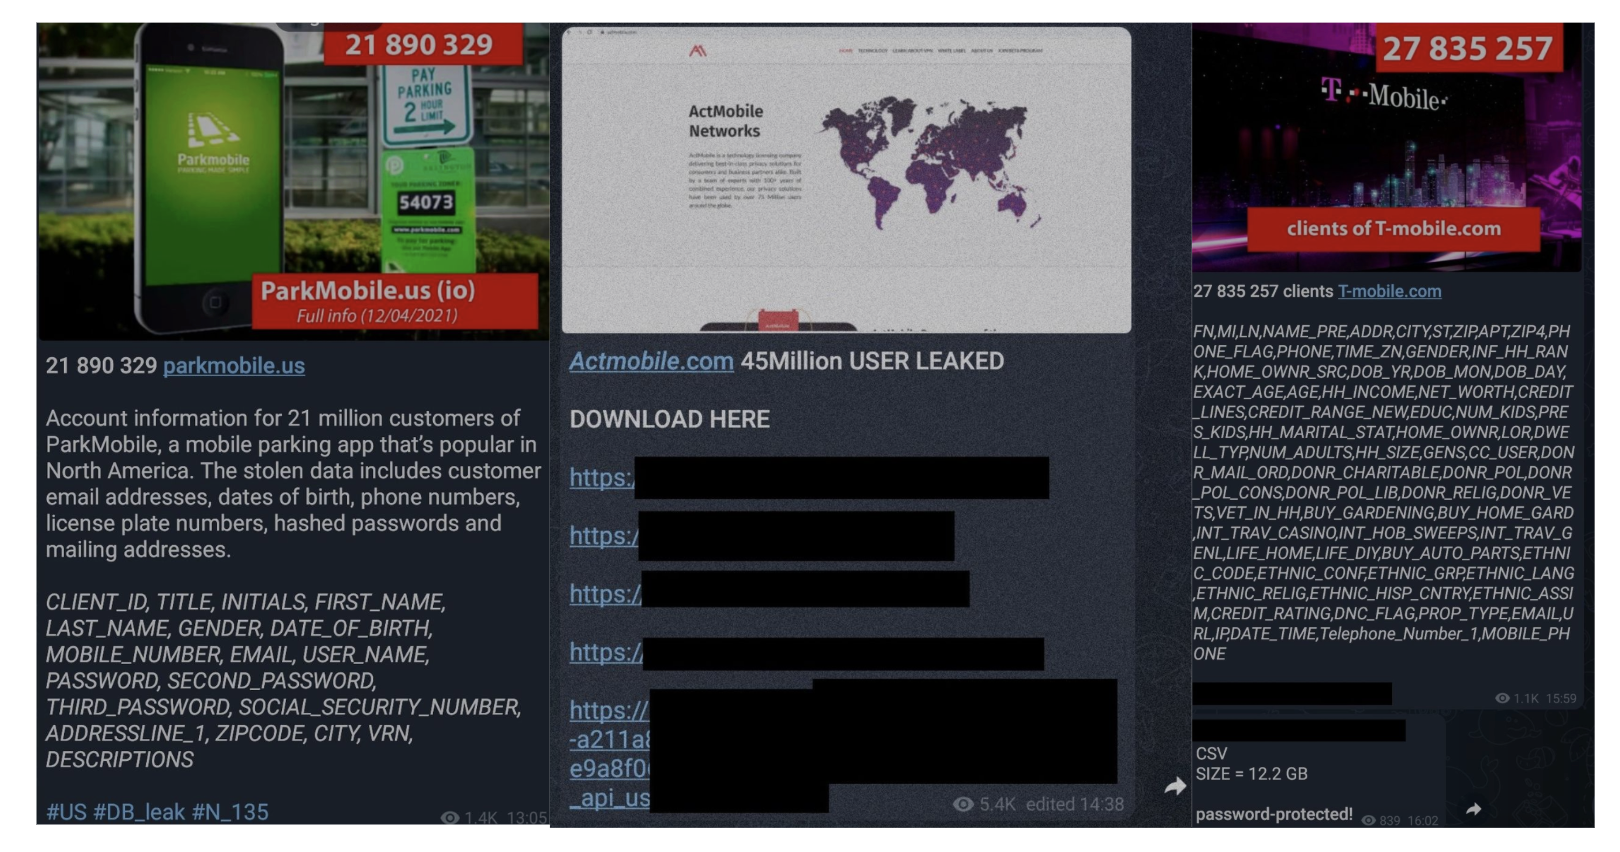
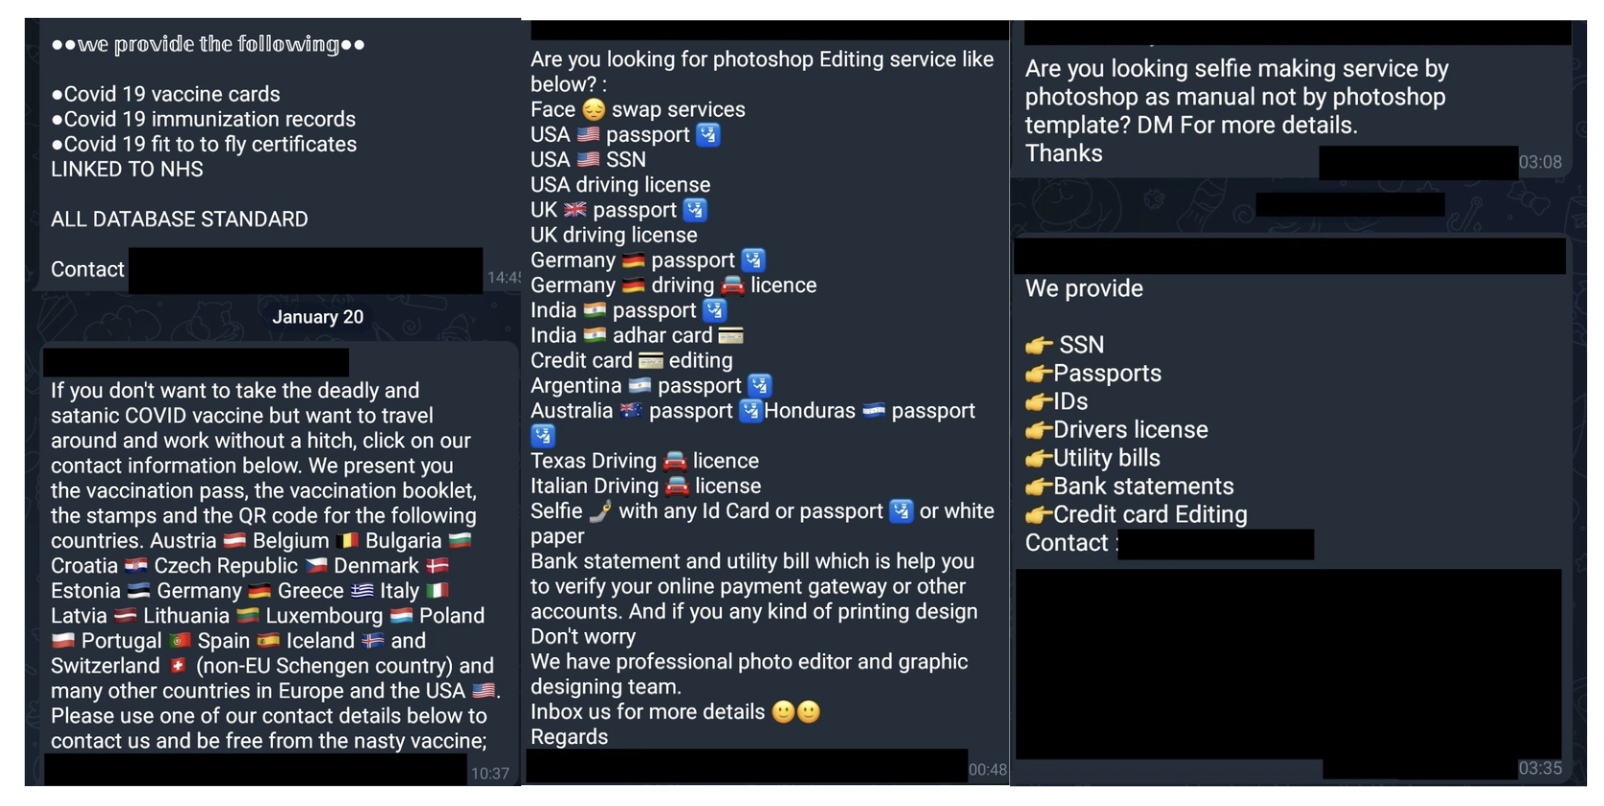
Inside active Telegram carding channels
While carding operations may seem abstract, they’re very real and happening right now.
Telegram has eclipsed 1 billion active users globally. Security researchers estimate that thousands of dedicated carding channels operate on the platform, with some channels boasting 50,000+ members. A 2023 Recorded Future report identified over 1,200 active Telegram channels dedicated to financial fraud, with daily transaction volumes estimated in the millions of dollars.
Here are the types of things law enforcement and security researchers are actually finding inside these channels:
Risks & legal consequences
Engaging in Telegram carding is highly illegal and carries severe penalties enforced worldwide.
Threat actors face legal exposure and prosecution despite believing Telegram keeps them anonymous. Investigators trace perpetrators through transaction logs, IP history, and cross-border cybercrime operations.
Convictions typically result in heavy prison sentences, fines, and victim restitution.
For example, from the Department of Justice:
A member of “Noir’s Luxury Refunds” was sentenced for participating in a fraud conspiracy organized through Telegram that targeted retailers nationwide.
FAQ about Telegram carding
What information do carders need to commit fraud?
Carders need the card number, CVV, expiration date, and stolen credential details obtained from stealer logs, data breaches, and dark web forums.
How do carders avoid detection when making purchases?
Carders utilize fake IPs, drop addresses, non-VBV cards, and carding bots to minimize exposure.
Why is cryptocurrency carding particularly dangerous?
Crypto carding lets threat actors rapidly convert stolen financial data into digital assets using low-verification exchanges.
Can law enforcement actually catch people using Telegram for carding?
Yes. Authorities trace financial records, logs, IP histories, and criminal network infrastructure to arrest cybercriminals.
What’s the difference between service carding and online store carding?
Online store carding targets retail goods, while service carding targets subscription apps and platforms to resell access across Telegram groups.
How do businesses detect carding attempts in real time?
Security teams use Telegram monitoring, dark web monitoring, and cyber threat intelligence to detect compromised credentials and leaks.
How can businesses protect against Telegram carding?
Organizations can strengthen defense against carding by implementing:
- Multi-factor authentication (MFA) across customer portals.
- Continuous monitoring systems for unusual transaction patterns.
- Comprehensive dark web monitoring and Telegram monitoring to flag compromised credentials and stealer logs.
- Partnering with cybersecurity providers to detect and remove threats before they’re exploited.
Advanced solutions like real-time threat detection platforms scan the internet to identify fraudulent sites and compromised credentials before damage occurs. Phishing detection services using AI algorithms analyze websites and emails to identify and block threats in real time, preventing the credential theft that enables carding attacks.
Real-time threat detection with Bolster AI
Bolster AI’s dark web monitoring tracks the Telegram channels where cybercriminals buy, sell, and announce fresh data leaks, giving security teams an early warning when customer or employee credentials surface.
Phishing Detection and Mitigation with Checkphish
Checkphish, a service by Bolster, focuses on detecting and mitigating phishing threats. It uses advanced AI algorithms to analyze websites and emails for signs of phishing, helping businesses identify and block these threats in real time.