The build-or-buy conversation about website takedown services almost always opens as a cost comparison, and that's the least useful place to open it. A fully loaded analyst salary set against an annual service fee produces a clean number for a budget request. It says nothing about whether a phishing site pointed at your customers comes down on a Saturday morning.
What decides the outcome is monthly volume, the jurisdictions your attackers register in, the hours your team can cover, the evidence you'll need if a case ever goes legal, and how much enforcement work you're willing to leave on someone's plate alongside their existing job. Both models can hit acceptable numbers under the right conditions. The real distinction is which failure modes each produces when volume spikes, when a campaign moves to a registry you've never contacted, or when the person who knows the escalation path goes on leave for two weeks.
Four jobs hide inside the word takedown
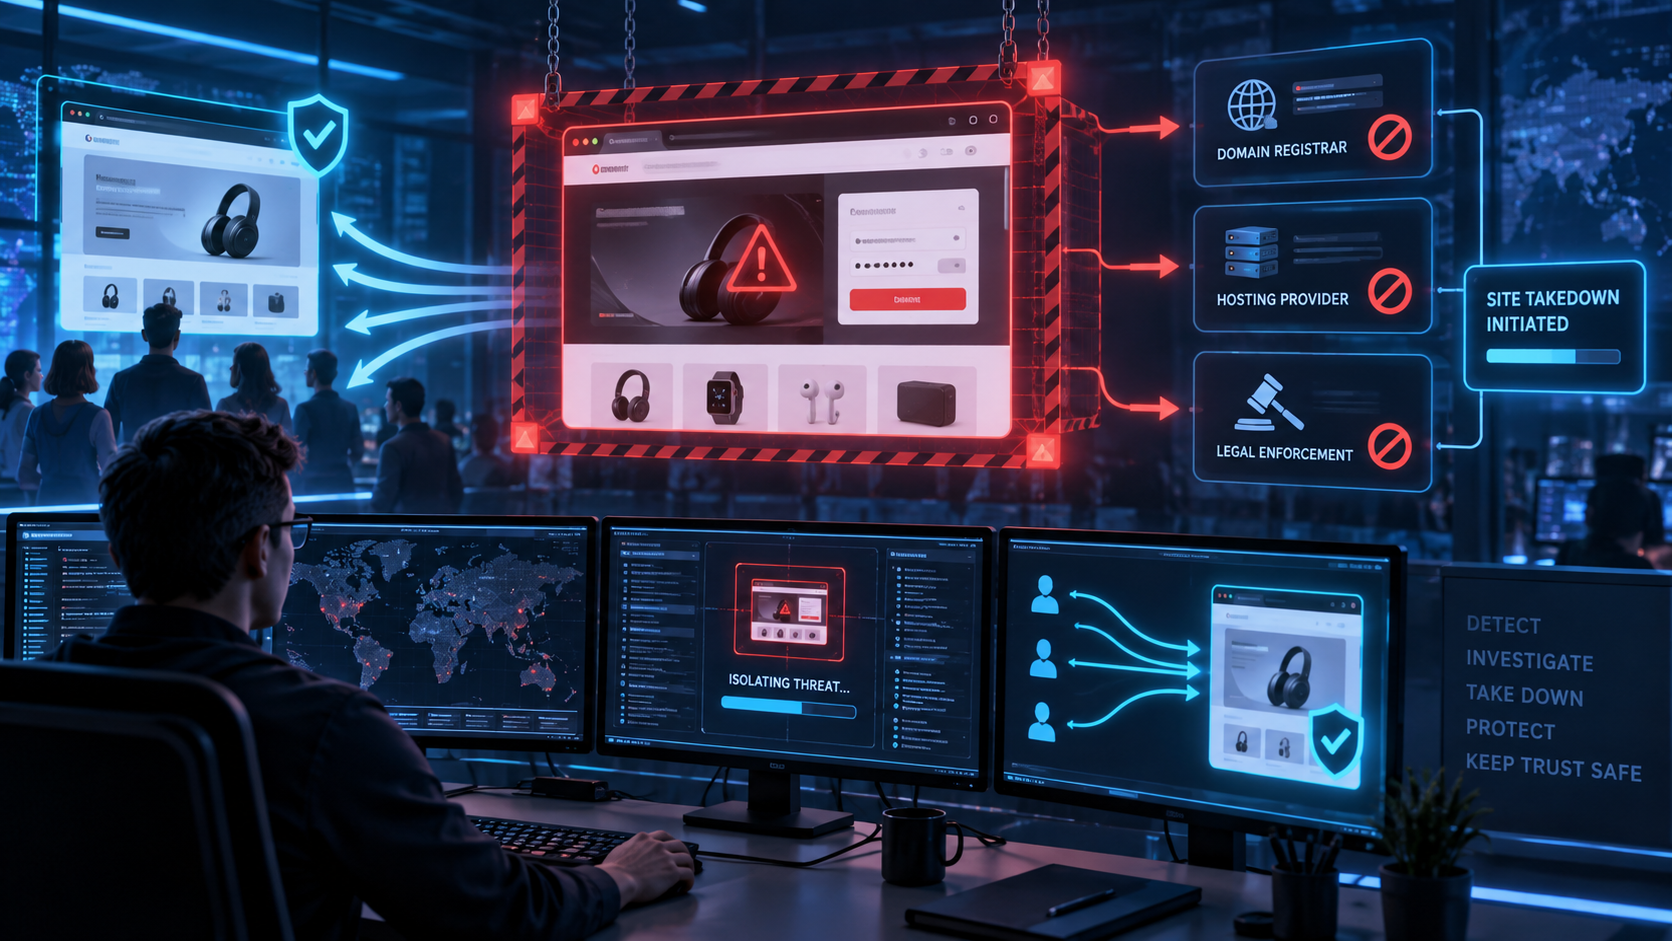
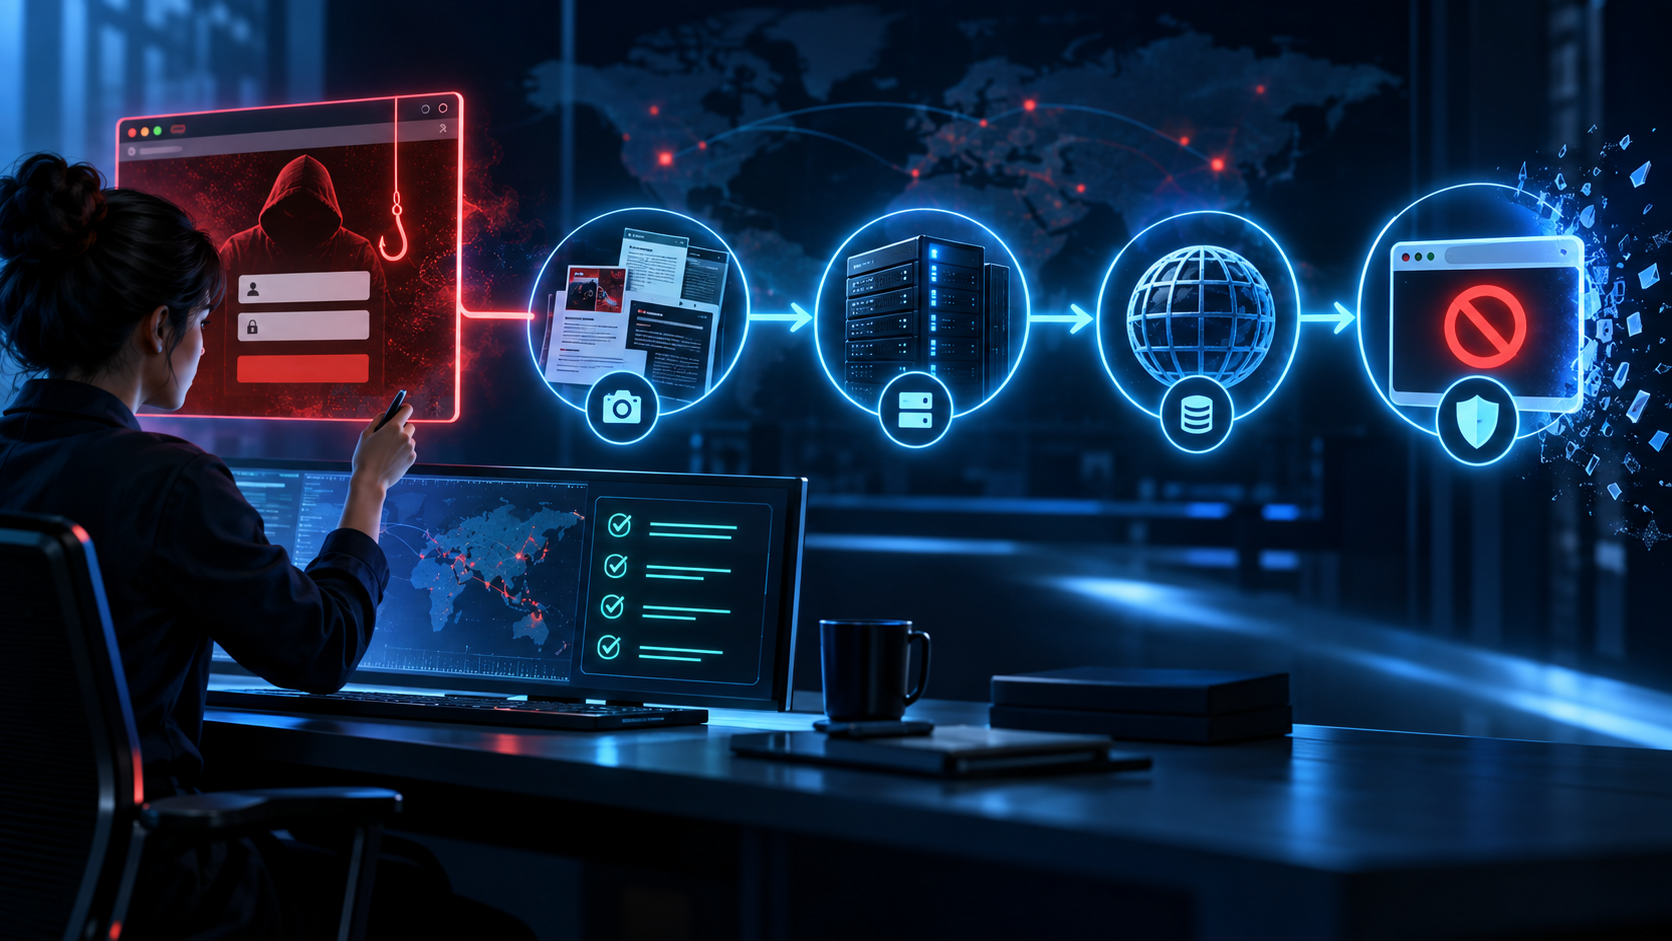
In-house and outsourced models break at different points along the chain, so it helps to separate the four activities that get collapsed into one word. Detection is finding the hostile asset, through lookalike domain monitoring, certificate transparency feeds, referrer logs, or a customer complaint that arrives before any of your tooling notices. Investigation is confirming the site is what it appears to be, mapping the host and registrar, and pulling the infrastructure fingerprints that connect it to the rest of the campaign.
Enforcement is the submission itself, routed to the party with both the authority and the willingness to act, with evidence packaged the way that party expects it. Confirmation is the unglamorous closing stage: verifying the site is actually offline, watching for the same content on adjacent infrastructure, and closing the record. Internal teams tend to be strongest at investigation, because they know the brand. Managed services tend to be strongest at enforcement and confirmation, because they do it all day.
The clock you're competing with
Whichever model you choose, it's racing the attacker's conversion window, and that window is short. A 2020 USENIX Security study led by Arizona State University researchers, covering a year of attacks against one major financial brand, found that detection by anti-phishing entities came nearly 9 hours after the first victim visit on average, by which point 62.73% of victims had already visited the page. The average attack ran about 21 hours between its first and last victim.
That reframes what the two models are competing on. A service level written into a policy document doesn't set the remediation window; the attacker's conversion speed does. The question for any model, internal or external, is who's awake and authorized to submit when the alert fires at 2 a.m. on a Sunday, and how long the evidence package takes to assemble once they are.
Volume makes the window harder to hit. The Anti-Phishing Working Group recorded 3.8 million phishing attacks across 2025, and the FBI's Internet Crime Complaint Center logged 191,561 phishing and spoofing complaints in 2025, inside a year that produced more than 1 million complaints and $20.9 billion in reported losses. Your slice of that is what the program has to absorb without the rest of the security function noticing.
Volume, and the overhead that doesn't shrink
Monthly volume is the cleanest decision variable, because each takedown carries a fixed administrative cost that doesn't fall as volume grows. Intake, triage, evidence capture, submission formatting, abuse desk follow-up, verification, and internal reporting all consume analyst attention per incident, however similar this domain is to the last 40. At a handful of incidents a month that overhead disappears into the working week. At dozens it becomes the working week, which is when detection quality quietly degrades because the same person is doing both jobs.
Campaigns also arrive in batches rather than one at a time. Interisle's Phishing Landscape 2025 study found that 37% of phishing domains were registered in bulk, across more than 70,000 bulk registration sets at 174 registrars. An in-house model sized for your average month meets its real test the week an operator registers 60 lookalikes at once.
Two questions settle this variable better than any published threshold. How many hostile sites did you act on last quarter, and how many did you learn about afterward that you never acted on at all? The gap between those numbers is the volume you're actually carrying.
Jurisdiction: gTLD abuse desks and everything else
Where your attackers register decides how much leverage you have. Since April 5, 2024, amendments to ICANN's Registrar Accreditation Agreement and base gTLD Registry Agreement have required ICANN-accredited registrars to confirm receipt of abuse reports and, when they hold actionable evidence that a domain is being used for phishing, to promptly take mitigation action; ICANN's compliance advisory spells out what that means in practice. The obligation covers generic top-level domains only, so for .com and the newer gTLDs there's at least a contractual duty to act and a shared definition of actionable evidence, even though the advisory is explicit that response times vary.
Country-code registries set their own policies, and they're a different operating environment: local presence requirements, national business hours, language expectations, and forms that assume a domestic legal representative. Interisle found that ccTLDs accounted for 11% of reported phishing domains, and that 40% of those were compromised legitimate domains rather than malicious registrations, which means the remedy has to be narrower and the conversation with the registry longer. An internal team that performs well on .com submissions can find its numbers collapsing the moment a campaign relocates to a registry it has never contacted.
The same study found that new gTLDs made up 11% of the domain market but 51% of reported phishing domains, which puts most phishing infrastructure with registries and registrars a .com-focused team may never have contacted, even before a campaign moves to a country code. Pull the registrar and TLD for your last 20 confirmed cases before you decide anything. If they're spread across operators you've never dealt with, jurisdiction is your deciding variable, not volume.
Standing with abuse desks is bought with volume
Relationship depth is the part of this work that can't be purchased quickly or built at low volume. Abuse desks respond faster to submitters whose previous reports were accurate, correctly scoped, and free of false positives, which is reputational credit accumulated across hundreds of interactions rather than a process you can document and hand to a new hire.
That's the specific weakness of sporadic in-house handling: an organization sending a few complaints a quarter never builds standing anywhere, and every submission is treated as a first submission. Outsourced website takedown services are largely a purchase of that accumulated standing, which is why their advantage widens as the jurisdictional spread of your attackers widens. Bolster AI's automated takedown flow runs on API relationships with registrars and hosting providers for the same reason: the request goes through a channel the provider has already agreed to accept and act on, with evidence attached rather than a bare complaint. Put the same question to any vendor, Bolster AI included: which registrars and hosts do they have that kind of relationship with, and what happens to a case at one they don't?
Buying has failure modes of its own, and they belong in the same conversation. Ask any vendor what authorization they need and how narrowly it can be scoped, how they tell a real impersonation from an aggressive affiliate before a request goes out, which registries their standing actually covers, and what evidence and case history you keep if the contract ends.
Coverage rate is the number that tracks exposure
Takedown success rate is the metric everyone reports, and it's defined narrowly: the share of submitted sites confirmed offline. The problem with using it as your program's health indicator is that you control the denominator. A program that only submits the easy, obvious, gTLD-hosted lookalikes will post an excellent success rate while the harder infrastructure stays up.
Campaign coverage is the harder question and the one that tracks customer exposure: of all the hostile assets that stood up in a campaign, what share did you find and act on? Operators rarely deploy a single site. They run parallel domains, staged redirect chains, regional variants, and replacement infrastructure prepared before the first suspension lands, and a team measuring only success rate can watch that number stay healthy while coverage erodes.
Hold both numbers side by side. An internal program with an excellent success rate and thin coverage is a weaker position than a managed workflow with a slightly lower success rate across a far larger share of the campaign. Coverage is a detection and investigation question, success rate is an enforcement question, and conflating them is how programs convince themselves they're winning.
Evidence you'll need later
Hostile sites are transient by design, and the record you'll need for a domain dispute or a civil action exists only if someone captured it while the site was live. That means timestamped captures of the landing page and each step of the credential flow, registration and DNS records as they stood at detection, hosting attribution, and enough infrastructure detail to link the domain to the wider campaign, all preserved before suspension makes the content unreachable.
Sporadic handling is where preservation quality degrades most predictably. An incident touched once a quarter by whoever is available rarely produces a consistent artifact set, and the problem surfaces later, when a pattern of repeat abuse from one operator becomes worth pursuing and the historical record turns out to be a folder of ad hoc screenshots with no chain of custody. Whichever model you choose, ask who captures what, in what format, and where it lives a year from now.
Continuity is the real staffing risk
A small internal program concentrates institutional knowledge in one or two heads. Registrar contacts, evidence formats that work, escalation shortcuts, and the judgment to distinguish a real impersonation from an aggressive affiliate all live with those individuals rather than in a system, so leave, illness, reassignment, or resignation removes the capability rather than degrading it gracefully.
Replacing that knowledge got harder in 2025. In the 2025 ISC2 Cybersecurity Workforce Study, 59% of respondents cited critical or significant skills needs, up from 44% in 2024, while 39% reported hiring freezes and 36% reported budget cuts. Ask what happens to your takedown queue during a two-week vacation, an unrelated major incident, or a resignation with two weeks' notice. If the honest answer is that it stops, the capability was never really built.
Verdicts by situation
The comparison resolves differently depending on where your volume, jurisdictions, and coverage hours sit, so the useful output is a set of conditional verdicts rather than a winner.
- Build in-house when volume is low and steady, attacker infrastructure concentrates on mainstream gTLD registrars, business-hours response is genuinely acceptable to the business, detection is already covered by an existing threat intelligence stack, and the analyst time is budgeted rather than borrowed.
- Buy a managed website takedown service when volume runs consistently above what one person can carry alongside another job, when campaigns spread across country-code registries, or when after-hours exposure is what actually costs you money.
- Run a hybrid when internal detection and investigation are already strong but enforcement is the bottleneck. Keep evidence capture and brand judgment in-house, and outsource submission, registrar escalation, and confirmation.
- Handle cases ad hoc only when abuse is genuinely rare, and set a review date, because abuse volume tends to grow with the business and ad hoc handling never builds standing with anyone.
Two situations deserve a sharper verdict than the conditions alone suggest. If attackers are running credential harvesting against your customers, speed should outrank organizational preference: the same USENIX study saw the earliest fraudulent transactions less than an hour after a victim visit, which makes a next-business-day internal target functionally cosmetic. If you're early in an internal build, decide in advance who handles enforcement while the team learns the phishing site takedown process and which abuse desks respond to what, rather than discovering the answer mid-campaign.
Instrument both numbers
Land on either model and measure it against success rate and coverage together, alongside honest reporting on jurisdictional gaps and single-person dependencies. Teams that review those together make the build-or-buy call on evidence instead of instinct, and they notice earlier when a model that used to fit has stopped fitting.
Bolster AI detects external threats including phishing sites, lookalike domains, fraudulent social accounts, fake mobile apps, fraudulent ads, and marketplace abuse, connects related infrastructure into a single campaign, and removes them. Detection and takedown run as one workflow rather than as two separate promises, with automation carrying the volume and Bolster AI analysts handling the cases that need judgment.
If you'd rather see a detection-through-takedown workflow run against your own volume and jurisdiction mix than model it on a spreadsheet, book a demo and bring the numbers from your last quarter.
TL;DR: The build-or-buy decision on website takedown services isn't a salary-versus-fee comparison. It turns on five things: how many hostile sites you see a month, where your attackers register them, who's awake when an alert fires, whether evidence gets captured before a site disappears, and what happens when the one person who knows the escalation path is on leave. In-house works when volume is low, attacker domains sit with mainstream registrars for generic top-level domains such as .com, and business hours are enough; a managed website takedown service wins as volume, jurisdictions, and after-hours exposure grow. The hybrid, internal detection and investigation with outsourced enforcement, deserves a price alongside either extreme.