Most teams compare domain monitoring services by how many lookalike domains each one finds, and they picture a lookalike as a typo. A joint CISA and FBI advisory on Scattered Spider shows why both habits fail. The group registered domains that added -sso or -helpdesk to a target's real name, in patterns like targetsname-sso[.]com, and used them to phish employees without misspelling anything. A tool tuned for character swaps misses names like these, and a tool that flags every string containing your brand buries them.
Choose a domain monitoring service by what reaches your alert queue and what happens to it next. A good service catches brand-plus-keyword registrations as well as typos, and it checks what a domain is doing before it alerts you. It connects each domain to the texts, ads, and social accounts sending traffic to it, and it moves confirmed threats into takedown in the same workflow. CISA notes that these specific Scattered Spider patterns haven't been recently observed, but they remain documented tactics that any group can reuse.
What a domain monitoring service actually does
Since match count is the wrong yardstick, the better one starts with what the service is supposed to deliver. Domain monitoring is a detection job: it watches new and existing domain registrations for names built to impersonate your brand, and it tells you which of those names matter. Investigation (working out what a domain hosts, who it targets, and what it's connected to) and takedown (getting the domain or its content removed by the registrar or host) are separate jobs, and a given service may do some of them or none.
Registrations are the right place to start. Interisle Consulting Group's Phishing Landscape 2025 study found that 77% of domain names used in phishing attacks were maliciously registered by cybercriminals. Most phishing domains exist because someone bought them for the purpose, so they appear in registration data before they appear in an employee's or customer's inbox.
That fact splits a buyer's evaluation into two halves. The first half asks whether the service sees the right registrations. The second half asks whether each alert arrives with enough context for your team to decide, and with a route to removal when the decision is yes.
How attackers build and use lookalike domains
The impersonating names a service watches for come in several documented shapes, and only one of them depends on a typo. The table below sets the Scattered Spider pattern beside the others that US authorities have described.
Pattern Documented example What it means for detection
Alternate spelling The FBI's IC3 warned in September 2025 that criminals were spoofing its own complaint site with alternate spellings of words. Character-level matching catches this pattern, which is why most tools start here.
Different top-level domain The same IC3 warning describes spoofed sites that use an alternative top-level domain to impersonate the legitimate one. Monitoring has to cover every top-level domain where your name could appear.
Brand plus trusted keyword CISA and the FBI describe Scattered Spider appending -helpdesk or a single sign-on term to the target's name, in patterns like targetsname-helpdesk[.]com. The name contains no error, so detection has to recognize your brand combined with words your employees trust.
Name of the service the victim expects In a 2024 toll scam, IC3 found texts linking to domains such as myturnpiketollservices[.]com, built to impersonate state toll services. Matching has to cover the service a victim expects to deal with, beyond your exact trademark.
The Scattered Spider row matters most for an evaluation because it defeats the cheapest kind of detection. The advisory says the group created domains for use in phishing and smishing against targeted organizations, so those domains reached employees through text messages as well as email. The domain was one component of the attack, and the delivery ran on a different platform.
The other FBI cases add detail about delivery. In the toll scam, IC3 received more than 2,000 complaints within about five weeks of early March 2024, and the phone numbers sending the texts changed from state to state. In an April 2025 warning about payroll, unemployment, and health savings account portals, the FBI reported that criminals bought search ads so a slightly misspelled URL appeared at the top of search results. In both cases the domain was the destination, and the traffic came from somewhere else.
Interisle's figures show the volume behind these patterns: the number of domain names used in phishing rose 38% to more than 1.5 million, the highest it has recorded. It also found that 37% of phishing domains were acquired through bulk registration services, which let attackers register large numbers of names at once.
Why domain monitoring alerts pile up
The variety in that table produces two opposite failures, and a single feed can suffer from both. Strict string matching, the kind that looks for swapped or doubled characters, misses brand-plus-keyword names like targetsname-helpdesk[.]com entirely. Loosening the match to catch those names flags every registration that contains your brand: a reseller's site, a fan page, a parked name, or an unrelated business that shares a word with you. An analyst then has to open each alert to find the few that host a login page.
Volume makes both failures worse. With phishing domains at Interisle's 1.5 million and more than a third of them bought in bulk, a feed that treats each registration as its own alert turns one campaign into many separate tickets. When Microsoft and a coalition that included Europol disrupted the Tycoon 2FA phishing-as-a-service platform, Microsoft seized 330 active domains that ran its control panels and fake login pages. Microsoft says Tycoon 2FA accounted for about 62% of the phishing attempts it blocked by mid-2025. A queue that receives those 330 domains as 330 unrelated alerts asks an analyst to rediscover the same operation hundreds of times.
Time adds the third pressure. The UK National Cyber Security Centre (NCSC) says takedown requests "could take anything between hours to days or even weeks." Every hour an analyst spends deciding whether an alert is real is an hour added before that removal clock even starts.
5 standards to use when you choose a domain monitoring service
Those two failure modes and the NCSC's takedown window translate into five standards. A service worth choosing meets all five, and you can test each one during an evaluation.
- It matches beyond typos. Detection should cover alternate spellings and other top-level domains, and also your brand combined with the terms your employees and customers trust. The concrete test comes from the Scattered Spider advisory: take your own name, append -sso, -okta, -servicedesk, or -helpdesk, and see whether lookalike domain and typosquatting detection surfaces those patterns.
- It finds threats on its own, early. The NCSC's guidance on choosing a takedown provider asks, "How do they discover attacks (other than ones reported by you the brand owner)?" Because 77% of phishing domains are registered for the purpose, registration is the earliest point to catch them. A service that waits for reports learns about a toll-style campaign after the texts have gone out and the complaints have arrived.
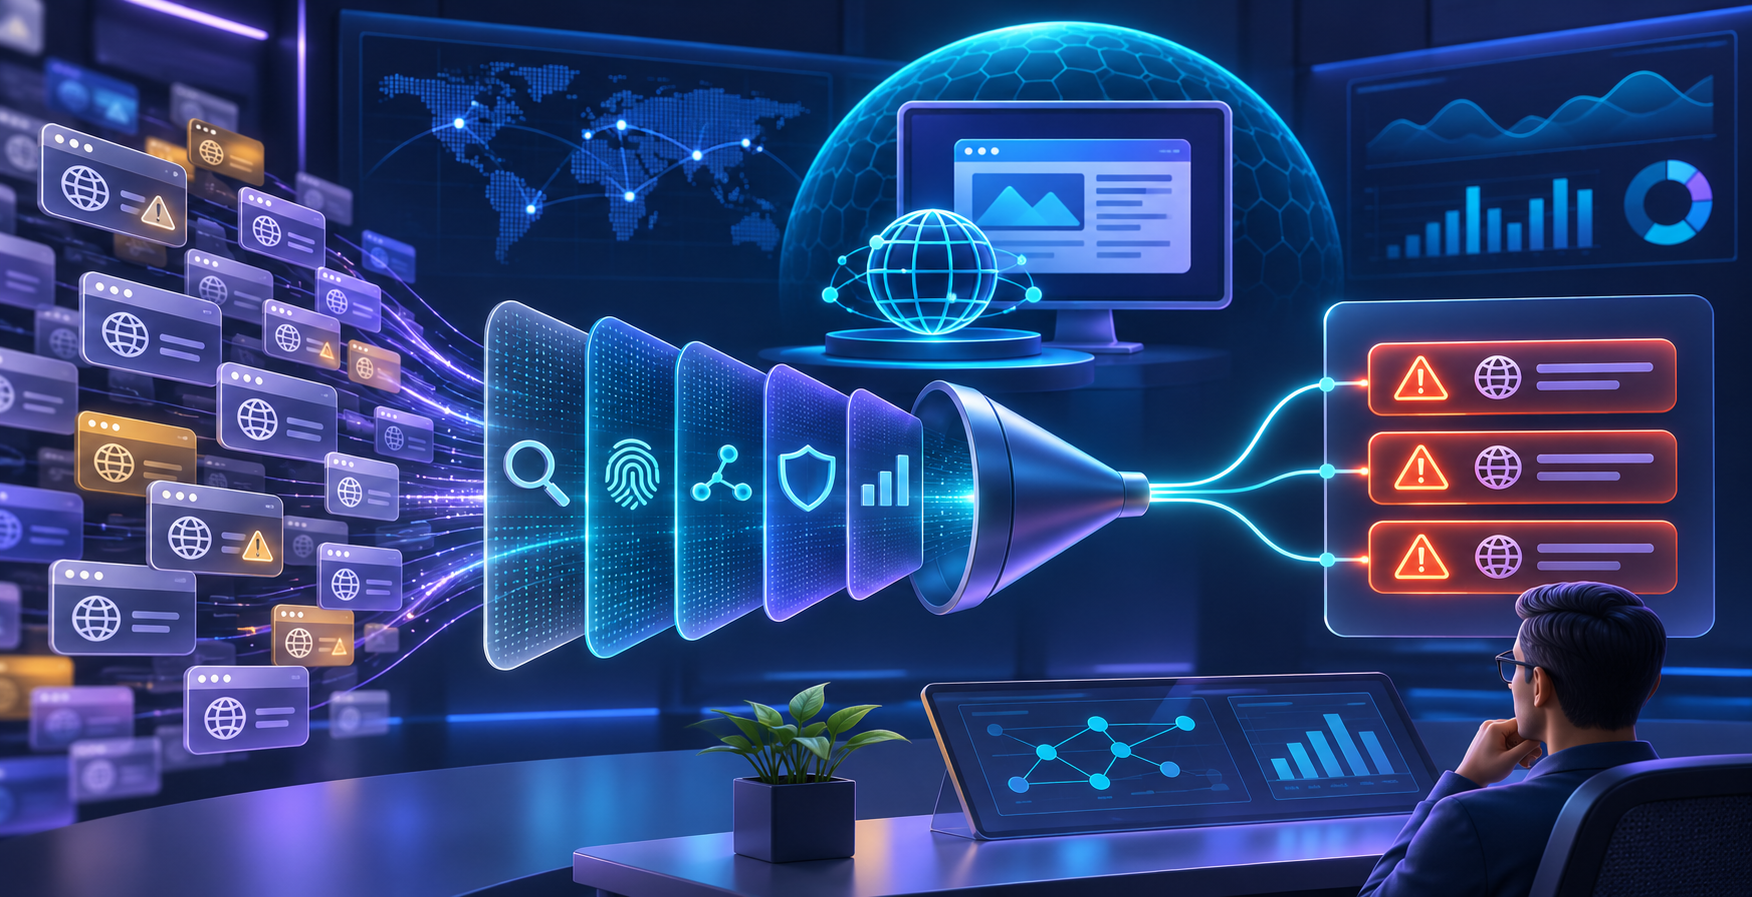
- It validates what a domain is doing before it alerts you. A match on your brand name is a lead, and an alert should be a finding. The service should check what the domain hosts (a login page, your logo, a payment form, a redirect, or nothing at all) and tell the analyst what it found, so parked and legitimate registrations stay out of the queue.
- It connects the domain to the rest of the campaign. The Scattered Spider domains reached employees through text messages, and the employee-portal lookalikes reached victims through search ads. A service should link each domain to related domains, social accounts, and ads, so an operation like Tycoon 2FA arrives as one campaign with its components attached rather than as hundreds of separate alerts.
- It acts on confirmed threats and keeps watching after removal. Confirmed threats should move into takedown in the same workflow, with submission to browser and security blocklists to reduce harm while removal is pending. Monitoring should continue after removal, so a domain that comes back is caught again. The NCSC also suggests asking whether a provider has established relationships with hosting providers and registrars around the world, and whether it can use legal compulsion when a notice isn't enough. Put that question to every vendor you evaluate, because the answers vary and they determine where the hours-to-weeks window lands.
Where common approaches to lookalike domains fall short
Measured against those five standards, the approaches most teams use today each cover part of the problem and leave a specific gap.
- Defensive registration. Buying the obvious misspellings and top-level domains of your main domain closes some doors. It can't cover every combination of your name with words like sso or helpdesk, and Interisle's finding that 77% of phishing domains are registered fresh by criminals means the attacker picks the name you didn't buy. This approach misses the first standard.
- Manual searching. An analyst searching registration data on a schedule can find the names they think to look for. Against the volume Interisle documented, manual searches can't validate each match or keep up with bulk registrations, so they fail the second and third standards.
- Waiting for customer and employee reports. Reports from customers and employees are valuable signals, and every program should collect them. They arrive after someone has already received the message, which leaves the NCSC's first question unanswered.
- An alert feed with no takedown path. A feed that stops at detection leaves your team writing abuse reports one by one to registrars and hosts it has no relationship with. The NCSC's hours-to-weeks window then starts from whenever an analyst gets to the ticket.
Domain monitoring and takedown with Bolster AI
Each gap in the previous section corresponds to a part of the workflow Bolster AI has built. Bolster AI is a digital risk protection platform that detects, investigates, connects, and removes external threats that impersonate trusted brands, and domain monitoring is one part of that workflow.
Detection of lookalike domains and typosquatting. Bolster AI's Domain Monitoring and Takedowns product watches for lookalike domains, typosquatting, and malicious domain infrastructure. That coverage addresses the first two standards: matching beyond typos and finding registrations before anyone reports them. Put the Scattered Spider test to Bolster AI the same way you would to any vendor, using your own name with the help-desk and single sign-on terms appended.
AI-driven analysis with analysts in the loop. Bolster AI uses machine learning, large language models, and computer vision to analyze potential threats. Automation carries the volume, and Bolster AI analysts stay in the loop for edge cases and complex threats. Test it against the third standard by asking to see what an alert on one of your own lookalikes tells your team about what the domain hosts.
Connected campaign context. A lookalike domain rarely works alone, as the smishing texts and search ads in the FBI cases showed. Bolster AI's social media monitoring covers impersonation and fraud across social platforms with its own takedown workflows, and its digital risk protection solution covers continuous monitoring and response across the external threat surface. A domain and the fake profile promoting it can then be handled as parts of one campaign, which is the fourth standard.
Takedown with monitoring afterward. Bolster AI's automated takedowns handle enforcement for confirmed phishing and scam threats, including submission to global blocklists, and they continue monitoring after the takedown so a threat that returns is caught. That combination covers the fifth standard and removes the step where an analyst files abuse reports by hand.
Bolster AI has limits worth stating plainly. No service, Bolster AI included, can stop a criminal from registering a domain in the first place, and most phishing domains are registered for exactly that purpose. Removal also depends on registrars and hosting providers that Bolster AI doesn't control, and the NCSC's hours-to-weeks range describes that dependency.
None of this replaces the controls you already have. Defensive registrations still protect the names you own, and email authentication still protects your own sending domain. Neither one reaches a domain that someone else registered and is using to target your employees or customers, and that external infrastructure is where Bolster AI does its work.
What to bring to a domain monitoring evaluation
The Scattered Spider domains from the opening contained no typo, so a vendor's count of lookalikes found tells you little about how its service will handle them. The useful test is what happens in your queue when a brand-plus-keyword registration aimed at your own name shows up: whether it arrives validated, connected to its campaign, and on a path to removal. New registrations keep arriving, so the service you choose becomes a standing part of your team's workflow.
Bring those brand-plus-keyword patterns to every demo, along with the cases your current process couldn't close, and judge each service on what its queue does with them.
Bolster AI detects external threats including phishing sites, lookalike domains, fraudulent social accounts, fake mobile apps, fraudulent ads, and marketplace abuse, connects related infrastructure into a single campaign, and removes it. Detection and takedown run as one workflow rather than as two separate promises, with automation carrying the volume and Bolster AI analysts handling the cases that need judgment.
Bring your own lookalike domains and hardest open cases to a custom demo built around threats to your organization. You'll see how Bolster AI turns them into campaigns your team can act on.
Frequently asked questions
How do I take down a fake or lookalike domain?
Confirm what the domain hosts and capture evidence, then send abuse reports to the registrar and the hosting provider, and submit the URL to browser blocklists so fewer people reach it while the report is pending. The NCSC says takedown requests can take anywhere from hours to weeks, and it notes that many takedown notifications aren't legally compelling. Bolster AI's automated takedowns handle enforcement and blocklist submission for confirmed phishing and scam threats, then keep monitoring after removal.
What should I do if someone registers a domain similar to my company's?
Check what the domain is doing before you act. A parked name with no content may only need watching, while a domain hosting a login page, your logo, or a payment form is a candidate for takedown. Look for what sends traffic to it as well, such as texts, search ads, or social accounts, because in the FBI cases above the domain was only the destination.
Is typosquatting illegal?
The answer depends on the jurisdiction and on how the domain is used, so it's a question for your counsel. Operationally, a domain hosting phishing can be reported to its registrar and host on abuse grounds, which is a separate route from a legal claim. The NCSC suggests asking takedown providers whether they can use legal compulsion when an abuse notice isn't enough.
Should we defensively register misspellings and other TLDs of our domain?
Registering the most obvious misspellings and top-level domains of your main domain is a reasonable baseline. It can't keep up with the brand-plus-keyword pattern from the Scattered Spider advisory, because the combinations of your name with words like sso or helpdesk have no practical limit. Interisle found that 77% of phishing domains were registered by criminals for the purpose, so monitoring new registrations has to cover what defensive registration leaves open.
How do I monitor my domains for typosquatting before attackers use them?
Watch new registrations for alternate spellings, other top-level domains, and your brand combined with trusted terms, then check what each match hosts before it reaches an analyst. Keep watching names that look parked, because what a domain hosts can change after registration. Bolster AI's domain monitoring covers lookalike domains and typosquatting and moves confirmed threats into takedown, with Bolster AI analysts reviewing the cases that need judgment.