Most takedown vendors describe themselves in almost identical language. They detect fake sites, they get them removed, and they do it fast. Read three vendor pages back to back, and you’d struggle to tell them apart.
The differences are real, but they don’t show up on a feature list. They show up in what a vendor counts as finished, what happens on the cases nobody wants, and what your bill looks like in a bad month.
Volume is part of why this decision matters, and the annual picture has been flat at a high level rather than spiking. The Anti-Phishing Working Group recorded 3.8 million phishing attacks across 2025, up slightly from 3.76 million the year before, and 971,181 in the first quarter of 2026. Verizon’s 2026 Data Breach Investigations Report found the human element in 62% of breaches, with phishing accounting for 16% of initial access vectors.
Numbers at that scale mean you won’t win this by being careful. You’ll win it by removing things quickly and repeatedly, which is a question of who you hire and how they work.
Here’s what to actually ask.
Start with how threats reach you today
Before you talk to anyone, get honest about your baseline. Pull the last quarter of impersonation cases and answer one question: how did you find out?
If most of them came from a customer complaint or a support ticket, you don’t have a takedown problem. You have a detection problem, and buying faster enforcement won’t fix it. You’ll just remove things more quickly once somebody else notices them, which is a real improvement but a much smaller one than you’re about to pay for. That distinction changes what you’re shopping for, and vendors are happy to sell you either one without pointing out the difference.
Ask what “taken down” means to them
This question separates vendors faster than any other, and almost nobody asks it.
Some providers count a case as closed when they submit the abuse report. Others count it when the host confirms removal. Those two definitions produce identical-looking dashboards and completely different outcomes, because a submitted report isn’t a removed page, and the gap between the two is where your exposure actually lives. Get the definition in writing.
Then push on a second point: does a browser warning count as a takedown when the page is still live? Blocklisting is genuinely useful, and it protects people while a slow host makes up its mind. But it isn’t removal, and a vendor who blends the two in its reporting is telling you how it’ll handle your metrics later.
Detection sets the ceiling on everything else
No enforcement workflow can act on infrastructure nobody has found. Whatever a vendor’s takedown speed looks like, detection coverage is the number that caps it.
Coverage has two dimensions, and vendors tend to be strong on one and quiet about the other. The first is where they look. Web and lookalike domain registrations are table stakes, but campaigns also run through fake accounts on social platforms, app stores, marketplaces, paid ads, and criminal forums where kits and stolen credentials change hands. A vendor that only looks at the web isn’t covering less ground than the others by accident. It’s covering the part of the campaign that’s easiest to see, and leaving the parts that give the operation its reach.
The second dimension is how a vendor recognizes something as yours. A system that matches domain names catches a misspelling of your brand. It won’t catch a site on an unrelated domain that has copied your logo, your colors, and your login page pixel for pixel, which is what a competent operator builds. Find out whether detection works on visual similarity to your brand assets or only on text.
Then put the question that cuts through all of it. In the last 30 days, how many confirmed impersonations did this vendor find that our team had never seen? That number is worth more than any coverage claim.
Ask about the campaign, not the URL
A fake login page is rarely the whole attack. It usually sits inside something larger: an ad driving traffic to it, a social account lending it credibility, a lookalike domain registered alongside 40 others, and a mail server sending the lure. Remove the page on its own and the rest of it keeps working, because none of the surrounding infrastructure depended on that particular URL staying up. The operator points the ad at a replacement domain, and your team starts over on a case it thought was closed.
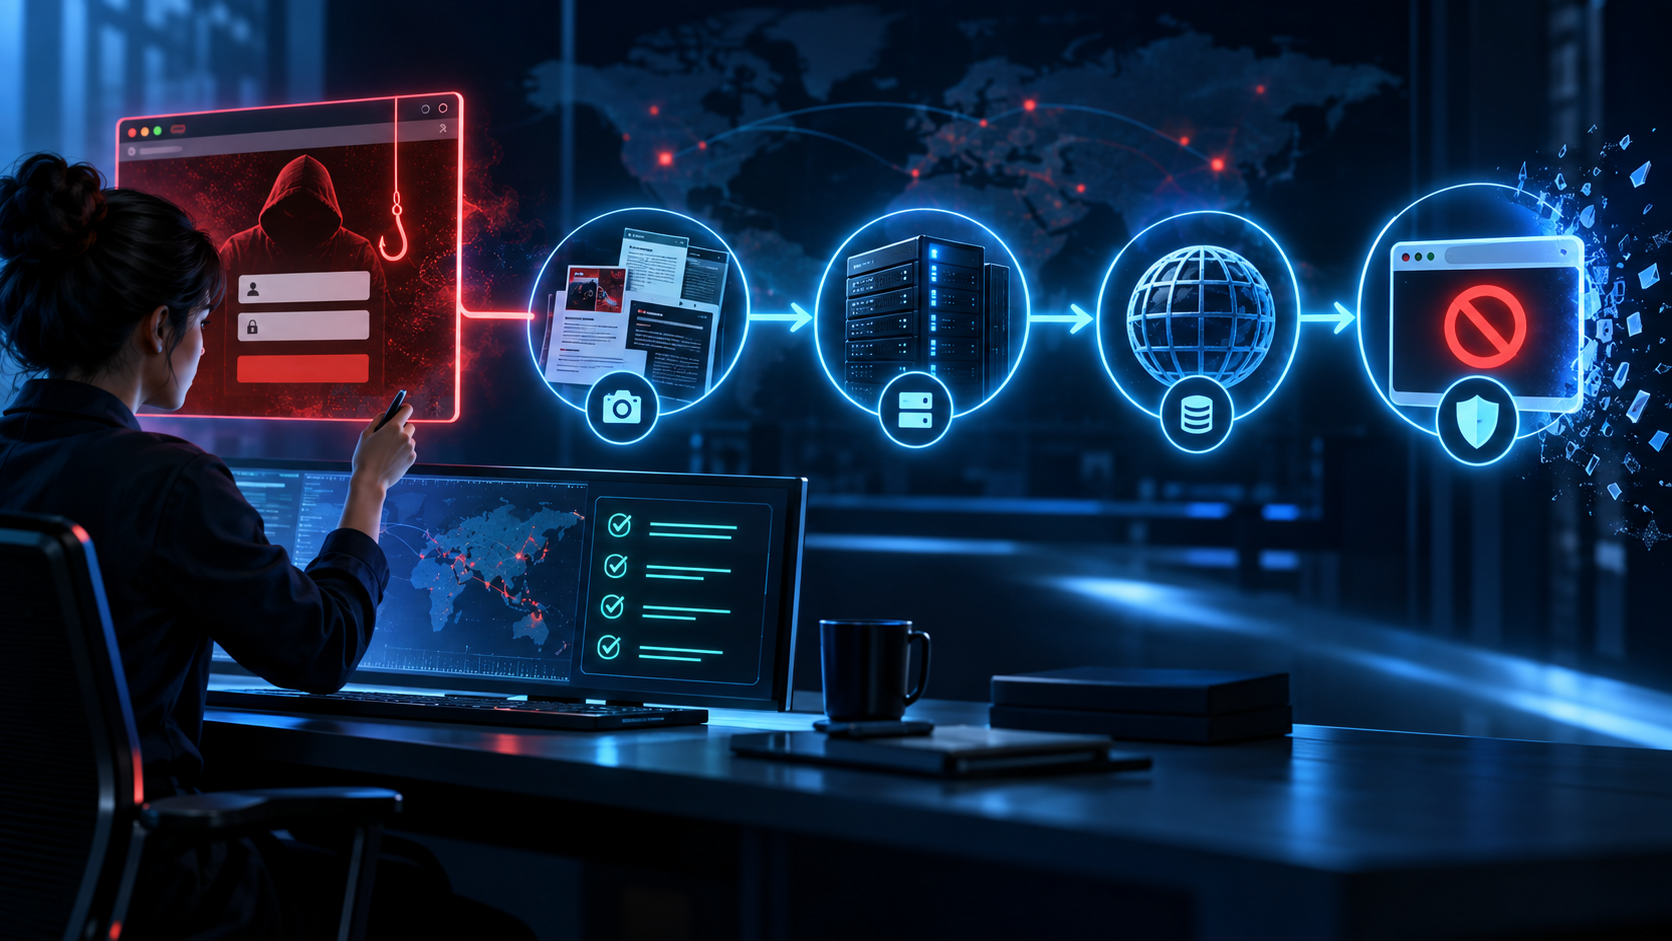
So find out how a vendor handles the connected pieces. Do they cluster related infrastructure and act on it together, or do they open a separate case for every URL you report? Do they keep watching after a removal, and for how long? If a campaign returns on new infrastructure next week, does that reopen the original case or start a fresh one? Our phishing site takedown guide walks through what that end-to-end process looks like when it’s built as one workflow.
That last detail sounds like paperwork. It isn’t. It decides whether your reporting shows you one operator hitting you five times or five unrelated incidents.
Find out what happens when nobody answers
Every vendor handles cooperative hosts well. That’s the easy half of the job, and it’s the half the sales conversation covers.
The informative question is what happens on the rest. Ask what they do when an abuse contact goes silent, when the host sits in a jurisdiction that doesn’t respond, or when the real origin is hidden behind a privacy service. These are the cases that consume disproportionate analyst time, and they’re the ones a capability matrix will never show you.
What you’re listening for is whether there’s a ladder at all, and who climbs it. A vendor should be able to describe the second request when the first goes unanswered, who else in the chain they can reach, and what they do to reduce harm while the page is still up. That last part is what your customers actually experience.
Blocklist submission is the usual answer there, and it’s worth knowing how quickly it happens, because it’s the one step that protects people before removal lands. Bolster AI handles that inside its automated takedown flow. Put these questions to us as well.
Push for the share of last quarter’s cases that landed in that difficult tail, and for one example they couldn’t resolve. How a vendor talks about a failure tells you more than any success rate.
Get legal comfortable early
Takedowns get submitted in your name. That makes your general counsel a real stakeholder, and discovering it late is one of the more common ways an evaluation stalls. Legal’s concern usually isn’t whether the product works; it’s exposure if a vendor removes the wrong thing on your behalf, so their questions run toward authorization and evidence rather than detection rates.
Bring legal in with two questions. What authorization does the vendor need from you, and how is it scoped? And when a removal gets challenged, what record exists of what was submitted, to whom, and when? Neither answer has to be perfect for a deal to proceed. Both need to be known before your general counsel sees the paperwork for the first time in week nine.
Check how the pricing behaves on a bad month
Pricing models look similar until you have an incident. Then they diverge sharply.
If enforcement is metered, a coordinated campaign that spins up dozens of domains turns a security event into a budget conversation, usually at the worst possible moment. It can also create quiet pressure on your team to report fewer threats, which is the wrong incentive to build into a security program.
So establish what a bad month costs. It’s worth confirming whether takedowns, user seats, implementation, and support are included or billed separately, and what happens if volume doubles. A model you can predict is worth more than a low headline number that moves when you need it most.
Make the demo run on your threats
A demo environment shows you the product working under conditions the vendor chose. Ask to see it working against yours instead. Bring cases you already know about, including two or three your team couldn’t resolve, and watch what comes back that you didn’t supply. That’s the detection gap closing, or not.
Push on false positives as hard as you push on catches, because a noisy queue eats the analyst hours the automation was supposed to give back. Get them to walk you through a weekend and an overnight, since attackers don’t wait for Monday triage. Judge the whole cycle rather than the first impressive result.
Take these into the vendor call
Six questions, in the order they’re worth asking:
- How do you define a completed takedown, and does a browser warning count?
- In the last 30 days, what would you have found that we didn’t?
- Do you act on the whole campaign, or on the URL we reported?
- What happens when a host doesn’t respond, and how often did that happen last quarter?
- What do authorization scope and the audit trail look like for our legal team?
- What does a bad month cost us?
If you’re still building the vendor list itself, our roundup of domain takedown services covers who’s in the category. This piece is about how to separate them once they’re all on your shortlist.
Bolster AI detects external threats including phishing sites, lookalike domains, fraudulent social accounts, fake mobile apps, fraudulent ads, and marketplace abuse, connects related infrastructure into a single campaign, and removes them. Detection and takedown run as one workflow rather than as two separate promises, with automation carrying the volume and Bolster AI analysts handling the cases that need judgment.
If you’d rather run these six questions against a live platform than a capability matrix, book a demo and bring the three cases your current process couldn’t close.
TL;DR: Takedown vendors describe themselves in nearly identical language, so feature lists won’t separate them. Six questions will: how they define a completed takedown, what their detection finds that yours doesn’t, whether they act on the campaign or the single URL, what happens when a host ignores them, how authorization and audit trails work for your legal team, and what a bad month costs. Ask those, and the differences show up fast.